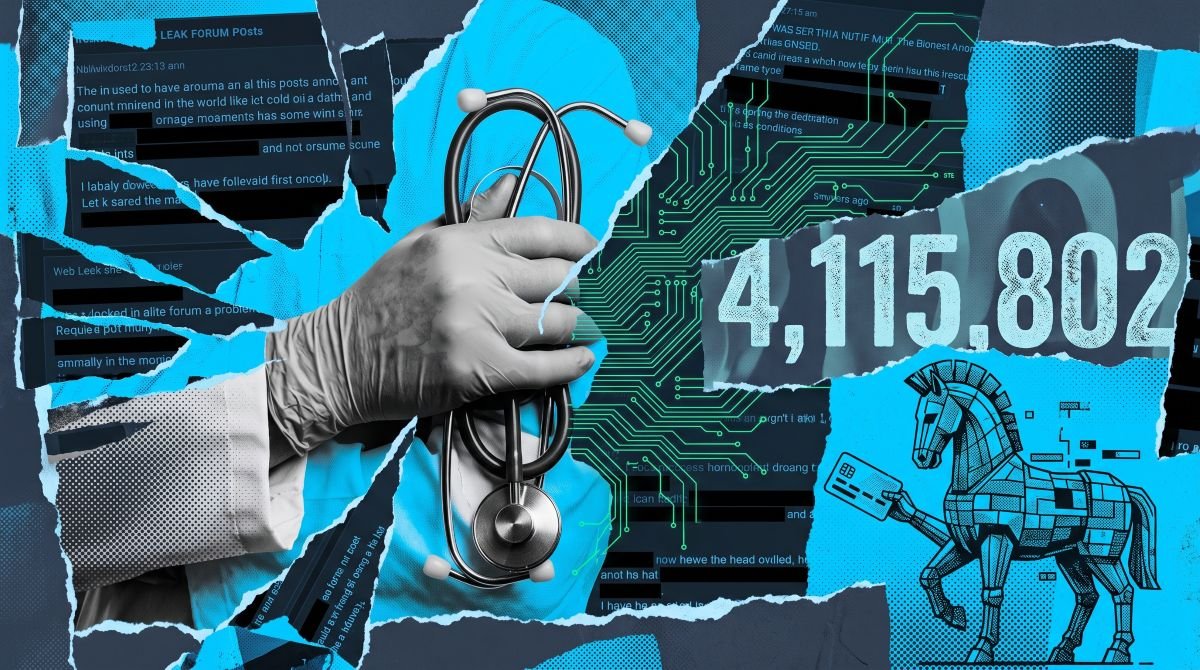
AdaptHealth confirmed on September 9 {that a} June cyberattack uncovered the well being information of 4,115,802 sufferers. That makes it one of many largest healthcare breaches disclosed this yr. The Pennsylvania-based dwelling medical gear supplier reported the quantity to the Division of Well being and Human Providers’ Workplace for Civil Rights, closing out a breach that the extortion group ShinyHunters claimed credit score for again in June, then quietly walked away from.
What AdaptHealth Confirmed
AdaptHealth provides sleep-apnea machines, oxygen gear, hospital beds, and mobility gadgets by roughly 680 places in all 50 states. Its personal account of what occurred, filed with the SEC on July 2, is pretty slim: a menace actor compromised the authenticated session of a third-party contractor by social engineering round June 5, then used that entry to succeed in AdaptHealth’s cloud-based enterprise functions, together with inside affected person administration techniques and doc storage.
The Leak Web site Itemizing That Vanished
The attacker obtained in contact on June 15 to demand a ransom in trade for silence. ShinyHunters added AdaptHealth to its darkish net leak web site round June 24 or 25. AdaptHealth determined the incident was materials on June 27 and filed the 8-Ok 5 days later. Notification letters went out in mid-August. This month, the corporate gave federal regulators the ultimate quantity: 4,115,802 folks, with names, contact particulars, demographic data, medical insurance data, and medical well being data uncovered, plus passwords tied to insurance coverage billing. No Social Safety numbers, AdaptHealth says, as a result of it doesn’t gather them within the affected techniques. No monetary account or cost card information both. And to date, no proof the stolen information has been used in opposition to anybody.
One factor didn’t make it into any of AdaptHealth’s personal statements. BleepingComputer reported this week that it may not discover an AdaptHealth entry on ShinyHunters’ extortion web site, which is normally an indication the group took the itemizing down itself. Neither facet has stated why, or whether or not cash modified fingers.
The Sample Behind It
A Six-Firm Warning From July
AdaptHealth isn’t an remoted case. Well being-ISAC, the healthcare sector’s information-sharing group, warned members on July 31 that ShinyHunters was operating a vishing marketing campaign in opposition to healthcare and health-adjacent corporations. It named six: Medtronic, iRhythm, OneMedical, DentaQuest, AdaptHealth, and Hims & Hers. The tactic hasn’t modified a lot since: name an worker, discuss them into resetting a password or enrolling a brand new gadget, use that foothold to get right into a single sign-on platform like Okta or Microsoft Entra, then pull information out of no matter cloud apps sit behind the login.
A Contractor’s Login, Not an Worker’s
AdaptHealth’s model of that assault has one wrinkle. The compromised session belonged to a contractor, not an AdaptHealth worker. Vishing aimed toward an organization’s personal workers can at the least be countered with coaching, phishing-resistant multi-factor authentication, and help-desk verification the corporate controls finish to finish. A contractor’s session sits partly exterior that. The group that owns the affected person information normally can’t see how the seller manages its personal credentials, and has even much less say in how briskly that vendor notices one thing is unsuitable.
It’s additionally the fourth ShinyHunters-linked breach in current weeks to observe this form: a vishing or social-engineering foothold, an SSO or cloud-app compromise, bulk exfiltration, then a ransom sized to the goal. ReliaQuest, Apollo International Administration, and McKesson all match that sample earlier this yr. AdaptHealth is the primary of the six Well being-ISAC-named healthcare targets to place an actual, federally filed quantity behind the declare, which makes it an honest benchmark for a way large this specific marketing campaign has gotten.
The Open Query
The disappearing leak-site itemizing deserves extra scrutiny than it’s getting. The FBI and CISA have each discouraged ransom funds for years, and most giant corporations say, on the report, that they don’t pay. However leak-site listings don’t normally vanish on their very own, and “no proof of misuse” is a distinct declare than “the info is gone.” Till AdaptHealth or ShinyHunters says extra, no person exterior that negotiation is aware of what occurred, and that hole between the general public non-payment place and the personal end result is strictly what retains this type of extortion worthwhile.
The Vendor Entry Downside
The contractor drawback is the lesson more likely to outlast this particular breach. Healthcare suppliers have spent years hardening their very own workers in opposition to social engineering whereas treating vendor and contractor accounts nearly as an afterthought, typically leaving them with standing entry as a substitute of scoped, time-limited credentials tied to 1 job. ShinyHunters has now proven, throughout six named targets, that it doesn’t have to breach a hospital or a medical provider immediately. It simply wants to search out the login no person’s watching.
Anticipate the subsequent few healthcare breach disclosures to hint again to a vendor’s compromised session relatively than a supplier’s personal community. Procurement and safety groups ought to begin asking, out loud, who else holds a key to their sufferers’ information apart from the folks treating them.