One of many largest cryptocurrency thefts from a single sufferer didn’t require breaking Bitcoin’s cryptography. Stolen knowledge, a reputable story and the sufferer’s cooperation had been sufficient to take over $245 million in digital foreign money from a single Washington, D.C. resident in August 2024.
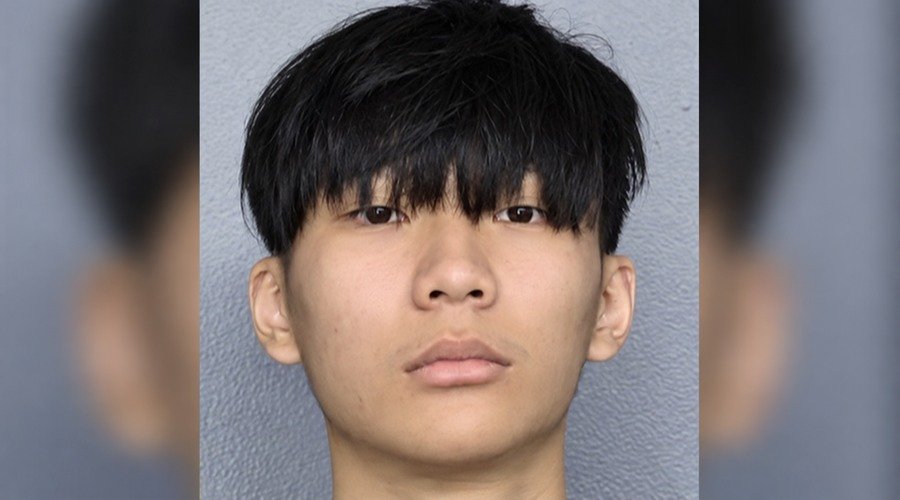
On September 8, 2026, Malone Lam, a 22-year-old Singaporean nationwide, pleaded responsible to a racketeering conspiracy cost within the US.
Prosecutors say the enterprise he helped run operated from October 2023 to at the very least Could 2025, hacking and shopping for databases of cryptocurrency holders, then analysing the information to establish high-value targets. In some circumstances, members broke into victims’ houses to grab {hardware} wallets.
Malone Lam, 22, a citizen of Singapore and up to date resident of Miami, pleaded responsible right this moment in connection along with his position as ringleader of a global cybercrime conspiracy that used social engineering to steal and launder cryptocurrency valued at greater than $245 million,… pic.twitter.com/R8Nnz9a7n6
— U.S. Lawyer DC (@USAO_DC) September 8, 2026
Fraud-as-Enterprise Mannequin
Lam’s enterprise labored as an organised enterprise with a transparent hierarchy and distinct roles. Members specialised in several domains, and every executed a particular a part of the operation.
Database hackers breached web sites and servers, or purchased stolen information on the darkish net, to construct lists of potential victims. Goal identifiers then combed the lists for the wealthiest prospects.
In a gaggle chat cited within the indictment, Lam provided co-defendant Conor Flansburg roughly 40 of these organised, stolen databases. Flansburg agreed to ship Lam and a fellow organiser a 20% reduce of any theft over $10 million, replying, “we hackin, all day on daily basis.”
A separate group of launderers transformed the proceeds into money, wire transfers and items. None of those roles required breaking Bitcoin’s cryptography, solely knowledge about who held the property, learn how to attain them and learn how to make the strategy plausible.
That division of labour will not be distinctive to Lam’s community. A 2026 International Initiative Towards Transnational Organized Crime research of Ukrainian rip-off name centres described an identical construction at nationwide scale: callers, closers, IT groups, HR, trainers, finance employees and directors, every dealing with one hyperlink within the chain.
Chart from International Initiative Towards Transnational Organized Crime report.
The purpose will not be the geography, however the working mannequin: social engineering has grow to be a staffed, segmented enterprise. A pockets doesn’t have to be breached immediately if attackers can establish the proprietor, assemble a convincing profile and induce the switch.
In 2025, Coinbase stated criminals had bribed abroad assist brokers to repeat buyer names, addresses, identification paperwork, transaction histories and steadiness snapshots.
The corporate stated no passwords or non-public keys had been uncovered, and that it could reimburse prospects tricked into transferring funds. Coinbase stated the stolen knowledge was supposed to make later impersonation makes an attempt extra convincing.
Lam’s enterprise, the Ukrainian name centres and the Coinbase breach have one factor in frequent: in none of them did a non-public key get compromised.
The frequent thread is that the assault started exterior the cryptographic layer. The weakest level was not the chain, however the data surrounding its customers.
Buyer Information Enters the Custody Perimeter
Non-public-key safety nonetheless issues, nevertheless it covers just one a part of the assault chain. A {hardware} pockets can not defend an proprietor whose identification, contact particulars and approximate holdings have already been assembled right into a goal profile. Cryptography can not set up whether or not a transaction was authorised freely, underneath deception or underneath bodily menace.
Buyer information at the moment are a part of the asset-security drawback. A steadiness snapshot, deal with, telephone quantity or assist be aware may help attackers select a goal and make an impersonation try credible.
Exchanges and custodians subsequently must deal with entry to buyer knowledge extra like entry to operational keys: tightly logged, narrowly permissioned and tougher to make use of after an unsolicited assist contact.
Larger-risk transfers can require cooling-off durations, further verification, or sign-off break up throughout multiple particular person; self-custody setups face the identical query if a single identifiable particular person can transfer all of the property without delay.
Lam’s enterprise ran on a provide chain of database hackers, goal identifiers, callers and launderers constructed round a simple break up of the proceeds.
A federal courtroom in Washington, D.C. is scheduled to carry a standing listening to within the case on December 8, 2026, when a sentencing date is anticipated to be set. That listening to would be the subsequent level at which the equipment behind the $245 million theft returns to public view.
One of many largest cryptocurrency thefts from a single sufferer didn’t require breaking Bitcoin’s cryptography. Stolen knowledge, a reputable story and the sufferer’s cooperation had been sufficient to take over $245 million in digital foreign money from a single Washington, D.C. resident in August 2024.
On September 8, 2026, Malone Lam, a 22-year-old Singaporean nationwide, pleaded responsible to a racketeering conspiracy cost within the US.
Prosecutors say the enterprise he helped run operated from October 2023 to at the very least Could 2025, hacking and shopping for databases of cryptocurrency holders, then analysing the information to establish high-value targets. In some circumstances, members broke into victims’ houses to grab {hardware} wallets.
Malone Lam, 22, a citizen of Singapore and up to date resident of Miami, pleaded responsible right this moment in connection along with his position as ringleader of a global cybercrime conspiracy that used social engineering to steal and launder cryptocurrency valued at greater than $245 million,… pic.twitter.com/R8Nnz9a7n6
— U.S. Lawyer DC (@USAO_DC) September 8, 2026
Fraud-as-Enterprise Mannequin
Lam’s enterprise labored as an organised enterprise with a transparent hierarchy and distinct roles. Members specialised in several domains, and every executed a particular a part of the operation.
Database hackers breached web sites and servers, or purchased stolen information on the darkish net, to construct lists of potential victims. Goal identifiers then combed the lists for the wealthiest prospects.
In a gaggle chat cited within the indictment, Lam provided co-defendant Conor Flansburg roughly 40 of these organised, stolen databases. Flansburg agreed to ship Lam and a fellow organiser a 20% reduce of any theft over $10 million, replying, “we hackin, all day on daily basis.”
A separate group of launderers transformed the proceeds into money, wire transfers and items. None of those roles required breaking Bitcoin’s cryptography, solely knowledge about who held the property, learn how to attain them and learn how to make the strategy plausible.
That division of labour will not be distinctive to Lam’s community. A 2026 International Initiative Towards Transnational Organized Crime research of Ukrainian rip-off name centres described an identical construction at nationwide scale: callers, closers, IT groups, HR, trainers, finance employees and directors, every dealing with one hyperlink within the chain.
Chart from International Initiative Towards Transnational Organized Crime report.
The purpose will not be the geography, however the working mannequin: social engineering has grow to be a staffed, segmented enterprise. A pockets doesn’t have to be breached immediately if attackers can establish the proprietor, assemble a convincing profile and induce the switch.
In 2025, Coinbase stated criminals had bribed abroad assist brokers to repeat buyer names, addresses, identification paperwork, transaction histories and steadiness snapshots.
The corporate stated no passwords or non-public keys had been uncovered, and that it could reimburse prospects tricked into transferring funds. Coinbase stated the stolen knowledge was supposed to make later impersonation makes an attempt extra convincing.
Lam’s enterprise, the Ukrainian name centres and the Coinbase breach have one factor in frequent: in none of them did a non-public key get compromised.
The frequent thread is that the assault started exterior the cryptographic layer. The weakest level was not the chain, however the data surrounding its customers.
Buyer Information Enters the Custody Perimeter
Non-public-key safety nonetheless issues, nevertheless it covers just one a part of the assault chain. A {hardware} pockets can not defend an proprietor whose identification, contact particulars and approximate holdings have already been assembled right into a goal profile. Cryptography can not set up whether or not a transaction was authorised freely, underneath deception or underneath bodily menace.
Buyer information at the moment are a part of the asset-security drawback. A steadiness snapshot, deal with, telephone quantity or assist be aware may help attackers select a goal and make an impersonation try credible.
Exchanges and custodians subsequently must deal with entry to buyer knowledge extra like entry to operational keys: tightly logged, narrowly permissioned and tougher to make use of after an unsolicited assist contact.
Larger-risk transfers can require cooling-off durations, further verification, or sign-off break up throughout multiple particular person; self-custody setups face the identical query if a single identifiable particular person can transfer all of the property without delay.
Lam’s enterprise ran on a provide chain of database hackers, goal identifiers, callers and launderers constructed round a simple break up of the proceeds.
A federal courtroom in Washington, D.C. is scheduled to carry a standing listening to within the case on December 8, 2026, when a sentencing date is anticipated to be set. That listening to would be the subsequent level at which the equipment behind the $245 million theft returns to public view.