

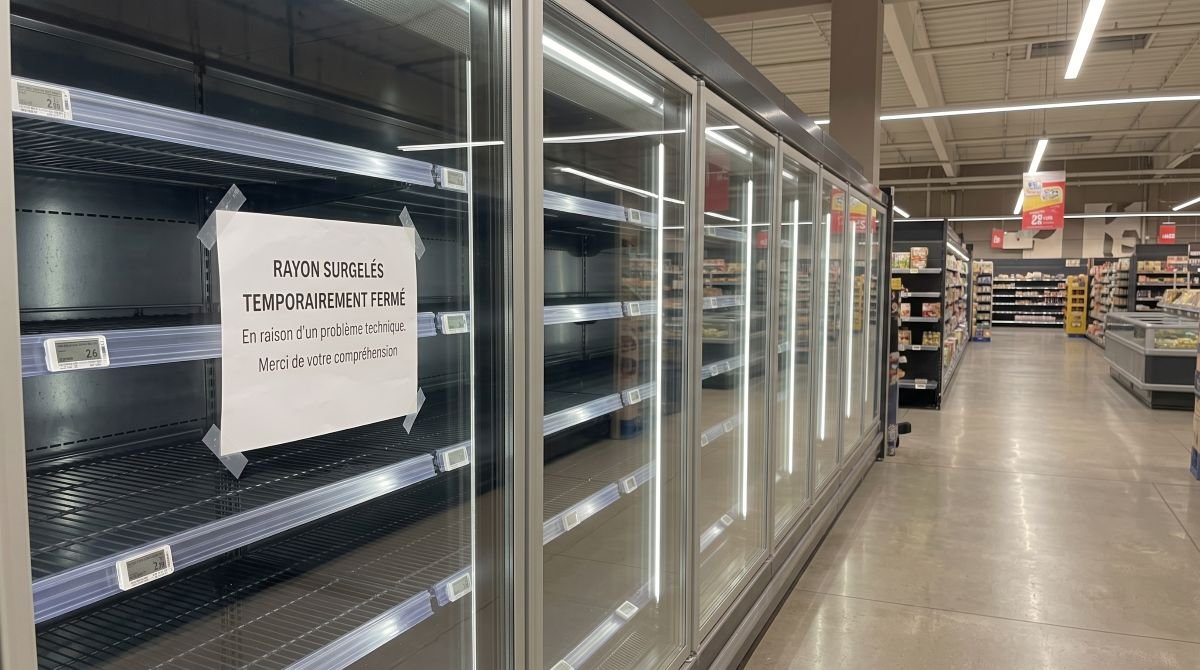
In a single day on 11 to 12 October, attackers took management of the refrigeration controllers in tons of of French supermarkets and drove cupboard temperatures as excessive as 50°C. Les Mousquetaires, the group behind Intermarché, says fridges at about 150 of its shops stayed that sizzling for six hours and that workers discarded the affected meals, in line with Reuters. As of 14 October, no group has claimed the assault, and neither French authorities nor the tools producer has mentioned how the attackers obtained in.
What Occurred, and How Massive It Is
Retailers confirmed the assault first. Dominique Schelcher, chief govt of Coopérative U, posted on Monday that cyberattacks had hit the refrigeration tools of a number of shops, and he known as the assault “unprecedented” and “unacceptable” (CNBC). Intermarché instructed AFP that affected shops must throw out all of the merchandise involved. Managers who arrived on Monday morning met a wave of sizzling air from the freezers, in line with the BBC, and BFMTV confirmed an ice cream freezer studying 26.5°C. Reuters reported that Paris resident Geert de Clercq watched workers at an Intermarché within the middle of town throw cartfuls of defrosted meals into a large trash container whereas melted ice cream spilled from damaged tubs onto the road.
The Paris prosecutor’s workplace opened an inquiry that its cybercrime part is working with the nationwide anti-cybercrime workplace, OFAC, to determine victims and tie them to the reported losses (Euronews, Sud Radio, each relaying AFP). It described a “large-scale” assault on related fridges at a number of main retailers. Prime Minister Sébastien Lecornu has instructed ANSSI, France’s nationwide cybersecurity company, to research, an individual in his workplace instructed Reuters.
Retailer counts differ by outlet and by day, and almost all of them come from the businesses. Reuters counted a minimum of 350 supermarkets by Tuesday and known as {that a} small fraction of France’s complete (Reuters, as carried by Interaksyon). Including up the chain figures, the BBC arrived at about 400 shops out of roughly 15,000 in France. France’s finance minister, Roland Lescure, instructed parliament on Tuesday that about 700 of the nation’s 10,000 supermarkets had been affected, in line with CBC. The 2 tallies use completely different denominators, and the protection doesn’t reconcile them. The desk collects what every chain, or press protection of it, has reported.
| Retailer | Reported impression | The place it comes from |
| Les Mousquetaires (Intermarché, Netto) | About 150 Intermarché shops per the group’s spokesperson; 150 to 200 per AFP; round 180 Intermarché and Netto shops per the group’s e mail to CNBC and the BBC. The BBC provides that about 100 extra shops had been disconnected from the web as a precaution. Some French experiences put the group complete close to 300. | Reuters; CNBC; BBC; AFP by way of Euronews; Bloomberg by way of The Subsequent Internet; Infosecurity Journal; Journal de l’économie |
| Coopérative U (Système U) | Fewer than 100 shops per AFP’s Monday report; greater than 100 per the BBC. | AFP by way of Euronews; BBC |
| Carrefour | 80 of its roughly 6,000 shops. | Reuters; BBC |
| Monoprix | About 5% of its shops. Reuters counts about 490 in France, the BBC says 400-plus. | Reuters; BBC |
| E.Leclerc | “A number of shops.” The group mentioned a refrigeration tools provider was hit. E.Leclerc and Auchan didn’t reply to Reuters. | AFP by way of The Hacker Information; Reuters |
Losses are tougher to pin down. Les Mousquetaires instructed CNBC it expects losses of “a number of million euros” and is ready for a court-appointed bailiff and insurance coverage specialists to provide firmer figures. Thierry Cotillard, Intermarché’s chief govt, instructed BFMTV the assault would price tens of thousands and thousands of euros nationwide in a single day, in line with Reuters. At retailer stage, BFMTV reported that two supermarkets in Alsace, an Intermarché and a Tremendous U in Haguenau, misplaced about €270,000 of inventory between them (BBC, Infosecurity Journal). Intermarché additionally warned that some insurance coverage contracts might not cowl one of these incident, so a part of the invoice might stick with the shops.
The fires are essentially the most disputed a part of the story. The Paris prosecutor’s workplace mentioned, as relayed by AFP, that there had additionally been départs de feu, or fireplace outbreaks, and Reuters reported that the assault led to meals losses and fires. The BBC experiences small fires in some locations. Les Mousquetaires instructed CNBC that overheated tools produced smoke in a few of its shops however that no fires have been reported. No public report names a retailer, a quantity or a trigger. ANSSI’s alert, posted by director normal Vincent Strubel on 13 October, instructed operators to disconnect the affected controllers and flagged a fire-start danger alongside misplaced inventory, in line with Options Numériques.
The Goal Is a Retailer-Large Refrigeration Controller
Many headlines say good fridges, which suggests a client equipment with a Wi-Fi chip. The affected tools is nearer to a thermostat with an online server hooked up: a store-wide controller that regulates chilly cupboards and chilly rooms, schedules defrost cycles and raises alarms. Reuters explains that grocery store chilly aisles sometimes run on management panels that handle a complete retailer’s fridges and freezers and may be reached over the web, which lets upkeep firms regulate them from wherever. Danfoss, the Danish producer, constructed the AK-SM and AK-SC sequence that French authorities have targeted on. Its AK-SM 800A system supervisor, for example, hosts an online interface the place directors monitor circuits, set temperature thresholds, evaluation alarms and handle customers, in line with Industrial Cyber’s description of Claroty’s analysis.
The web connection exists for a motive. Schelcher mentioned Coopérative U hyperlinks its fridges to the web in order that workers can monitor temperatures across the clock and catch an anomaly (CBC). That monitoring makes the publicity arduous to take away, as a result of disconnecting a controller additionally cuts the alert path that protects the inventory. Les Mousquetaires disconnected about 100 additional shops as a precaution, the BBC experiences, which exhibits the trade-off in apply.
Danfoss instructed information businesses on Monday that the affected items had been working outdated firmware or had reached finish of life and not obtain software program or safety updates (CBC). It has mentioned the affected tools included the AK-SM 800, declared finish of life in 2021, and the AK-SC 355, phased out in 2016, together with present AK-SM 800A items working outdated firmware (Cooling Submit). The historical past is awkward. Danfoss’s personal phase-out discover for the AK-SC 355, which carries a 2016 end-of-life date, names the AK-SM 800 sequence as its alternative. The BBC provides that Danfoss described the hit fashions as older ones whose safety software program couldn’t be up to date in opposition to a danger the corporate had recognized.
Danfoss additionally instructed Reuters it was conscious of incidents affecting a restricted variety of its refrigeration administration methods in France. Retailers rely shops and Danfoss counts methods, and the protection doesn’t reconcile the 2. The corporate will not be the one vendor concerned: in line with Reuters, ANSSI mentioned that refrigeration methods from Copeland and from Dixell, a Copeland model, had been additionally hit (TechNadu). Reuters experiences that Copeland acknowledged a vulnerability and mentioned it’s working with affected prospects (Reuters, as carried by Interaksyon). A Leclerc retailer within the Tarn misplaced its chilly chain on Tuesday and makes use of Dixell controllers, France 3 reported, as summarized by Options Numériques.
The mechanism issues as a lot because the model. Joshua Steinman, chief govt of commercial safety firm Galvanick, instructed Industrial Cyber that “defrost isn’t an exploit; it’s performance.” In his studying, essentially the most damaging instructions in industrial settings are sometimes reputable ones, so defenders want data of who reached a controller, what modified and whether or not anybody approved it.
How the Attackers Acquired In: What Is Identified and What Is Not
Nobody has publicly established the entry route. CERT-FR, the French authorities’s pc emergency response staff, issued alert CERTFR-2026-ALE-012 on 12 October reporting quite a few compromises of Danfoss AK-SM and AK-SC controllers and telling operators to disconnect them or filter entry to them (The Hacker Information). An individual in Prime Minister Lecornu’s workplace instructed Reuters that ANSSI had recognized a vulnerability in software program equipped by Danfoss. That account names no CVE and rests on one nameless supply.
Public analysis names the main suspects, although no one has tied them to this incident. A CISA advisory printed on 20 Could 2025 covers CVE-2025-41450, an authentication bypass within the AK-SM 800A: as a substitute of checking the configured admin password, the system accepts one generated from its personal date and time. Danfoss mounted it in model R4.2. A Danfoss advisory dated 1 August 2025 covers two extra flaws, a command injection that may result in distant code execution (CVE-2025-41451) and an Nginx configuration injection (CVE-2025-41452), each mounted in model 4.3.1. Claroty’s Team82 printed its technical write-up on 9 August 2026, in line with Reuters, and, in line with Bloomberg, discovered 1000’s of those controllers reachable from the web (The Subsequent Internet). The fixes had been public for 14 to 17 months by the night time of the assault.
Specialists quoted by Reuters and CBC lean towards the straightforward clarification. Three cyber specialists instructed Reuters the assault regarded straightforward to hold out, and CBC experiences that the specialists it consulted consider unapplied Danfoss updates and interfaces left open to the web made it potential, whereas noting that the precise mechanism continues to be unknown. Two cautions apply. Claroty’s work lined the present AK-SM 800A, whereas the AK-SM 800 and AK-SC 355 are the older items Danfoss says had been amongst these hit. And publicity just isn’t proof of compromise: SOCRadar, which counted Danfoss interfaces seen from France, mentioned so instantly (SOCRadar).
The publicity counts additionally fluctuate with the scanner. Predicta Lab’s Baptiste Robert discovered 2,752 uncovered Danfoss methods on Monday, 1,590 of them in France (BleepingComputer), and Reuters discovered a minimum of 4,500 Danfoss interfaces on Shodan on Tuesday with out with the ability to affirm what number of ran susceptible software program. French scanning agency Onyphe instructed Reuters that solely a small minority of uncovered items appeared to run the most recent software program.
Different routes match the identical information. Synacktiv, a French safety agency, instructed Options Numériques {that a} latest audit discovered refrigeration methods reachable from the web with no password in any respect, and that the geographic unfold of the assaults resembles opportunistic scanning for uncovered gadgets, although it mentioned that doesn’t affirm the strategy. Retailer statements additionally body the incident as a supplier-side occasion: Les Mousquetaires instructed CNBC that the assault hit a service supplier liable for managing refrigeration methods in a few of its shops. That will make a compromised upkeep channel as believable as a scanned system.
Attribution is equally open. A supply with information of the probe instructed Reuters that investigators are puzzled by the absence of a hacktivist declare or a ransom demand. Ken Munro of Pen Take a look at Companions known as it a primary cyber hygiene situation, mentioned amateurs may very well be accountable, and doubted {that a} state actor would hit solely a subset of French fridges. He additionally learn the lacking ransom demand as an indication that the attackers didn’t grasp the industrial losses they may inflict (Reuters, as carried by Interaksyon).
Why the Patch Has No Clear Proprietor
Regardless of the entry route seems to be, the general public statements already present a structural drawback, as a result of they level in numerous instructions. Danfoss says the items hit had been legacy merchandise with no updates, or present merchandise on outdated firmware, and that it has lengthy suggested prospects to maintain supported methods present and emigrate previous ones. Its personal cybersecurity steerage tells prospects to maintain its gadgets off the web, put them behind a firewall or VPN, change default passwords and run the most recent software program.
Retailers place the incident elsewhere within the chain. Les Mousquetaires instructed Bloomberg that the methods had been managed by Danfoss and that the provider, not the retailer, ought to file a criticism with the authorities (The Subsequent Internet). E.Leclerc mentioned a refrigeration tools provider was attacked (The Hacker Information). France’s retail federation, the FCD, has publicly known as on Danfoss for full transparency in regards to the incident (Reuters).
The remote-access design divides the job 3 ways. The producer publishes the repair, the retailer or its contractor has to put in it, and the contractor usually holds the distant entry. When a controller retired in 2021 continues to be working in 2026, which of the three was supposed to note?
Danfoss’s improve path is staged, in line with The Hacker Information: methods on 3.x transfer to 4.x first, and a controller on the 5.3.x package deal can’t be downgraded. Journal de l’économie cited replace complexity and value as obstacles to patching. These frictions assist clarify how a fleet this dimension can run behind its vendor’s updates, and the delay carries a value. Ritesh Kotak, a Toronto-based cybersecurity analyst, instructed CBC {that a} printed firmware replace exhibits attackers precisely which vulnerability to focus on, which is why he stresses putting in updates rapidly.
What No one Has Confirmed
The protection to this point mixes confirmed information with believable inference. As of 14 October, 5 factors stay open.
• The entry route. Whether or not attackers used a recognized flaw, an uncovered interface with weak or no authentication, or a compromised upkeep account, no one has mentioned. CERT-FR had printed no indicators of compromise as of 13 October (The Hacker Information).
• The attacker. No group has claimed duty, and no ransom demand has been reported. Investigators are puzzled by each information, in line with a supply who spoke to Reuters.
• The fires. The prosecutor’s workplace mentions them, the BBC experiences small fires in some locations, and Les Mousquetaires experiences smoke with out fires. No retailer, quantity or trigger has been printed.
• The unfold past France. Félix Aimé, a menace analyst at Sekoia, instructed Reuters that Spain, Portugal, Poland, Germany and Belgium additionally seem affected. SOCRadar famous that retailers in these nations had not confirmed incidents (SOCRadar).
• The Copeland and Dixell hyperlink. It rests on ANSSI’s assertion as relayed by Reuters. Copeland acknowledged a vulnerability and mentioned it’s working with affected prospects, however the protection reviewed right here provides no product-level element.
Two different incidents surfaced within the protection and will keep separate for now. Dutch retailer Ahold Delhaize took methods offline after a cybersecurity incident that started Sunday night. The corporate mentioned it noticed no motive to hyperlink the incident to the French assaults, and the Dutch NCSC doesn’t consider the 2 are related (Reuters, CBC). Reuters additionally famous that the French assaults resemble disruptions at a couple of dozen US navy commissaries in late August. Since then, Military CID’s cyber area workplace, the Air Drive Workplace of Particular Investigations and the Protection Felony Investigative Company have been investigating these outages, the place some freezers went into defrost mode (Stars and Stripes). No trigger or producer has been named, no findings had been introduced as of 30 September, and the Protection Commissary Company says separate freezer issues at 4 European shops had been unrelated to the US outages (Stars and Stripes).
The Regulatory Clock Is Already Working
Politicians moved rapidly to border the assault as a food-security situation. Lescure instructed parliament on Tuesday that there was no danger to the meals provide, however he acknowledged that the assault goes to the center of the nation’s meals safety (CBC). European Commissioner for Agriculture and Meals Christophe Hansen condemned it on X and mentioned the “weaponization of meals” has turn into a actuality (CNBC). Meals distribution has been a goal earlier than, CBC notes: JBS shut down operations in Canada, the US and Australia in 2021, and a 2025 assault on United Pure Meals led to shortages at Entire Meals.
The timing additionally makes this an early take a look at for EU product-security regulation. Since 11 September 2026, producers of merchandise with digital components have needed to report actively exploited vulnerabilities and extreme incidents below the Cyber Resilience Act, by means of the one reporting platform that ENISA operates. The principles name for an early warning inside 24 hours of turning into conscious, a fuller notification inside 72 hours, and a closing report afterward (European Fee). Legislation agency Jones Day reads the responsibility as protecting merchandise positioned available on the market earlier than the Act’s important obligations begin in December 2027, and notes fines of as much as €15 million or 2.5% of worldwide turnover for non-compliance (Jones Day).
Whether or not any producer has to file will depend on information that haven’t been printed: whether or not a vulnerability in its product was actively exploited, and whether or not it has cheap certainty of that. Danfoss declined additional touch upon Tuesday, and its safety advisories web page listed nothing in regards to the assault as of 13 October, in line with The Hacker Information. How the responsibility applies to a mannequin retired in 2021 is an open query that this case might pressure.
The operator facet strikes extra slowly. The French invoice transposing the NIS2 directive, whose sectors embody meals manufacturing, processing and wholesale distribution, was due for debate within the Nationwide Meeting on 7 October. The convention of presidents postponed it a day earlier, citing a busy agenda, and France missed the EU’s October 2024 transposition deadline (Subsequent.ink). For now, the EU responsibility already in pressure reaches the producers, whereas the operator-side guidelines in France are nonetheless ready for a parliamentary slot.
5 Checks for Operators This Week
The general public report already helps a brief record of actions for anybody working related refrigeration, regardless of the closing forensic report says.
1. Stock each refrigeration controller and remote-access gateway, together with items a contractor put in. File the mannequin, firmware model and end-of-life standing. Sophos’s Rafe Pilling advises figuring out uncovered and susceptible methods, validating patch ranges and assessing compensating controls (Industrial Cyber).
2. Take administration interfaces off the general public web, or restrict them to trusted addresses by means of a VPN. That’s the first instruction in CERT-FR’s alert, and it matches Danfoss’s personal steerage. Hold the monitoring itself: Schelcher’s shops join their fridges so that somebody can watch temperatures across the clock, and a VPN preserves that with out publishing the login web page.
3. Replace supported items and plan the alternative of end-of-life ones. Ask your vendor or contractor to substantiate in writing which firmware every retailer runs. If a unit might already be compromised, CERT-FR’s sequence is to limit community entry to service suppliers, manufacturing unit reset, apply all fixes, change secrets and techniques, examine accounts and reconfigure.
4. Put the contractor’s entry within the contract: who connects, from the place, with what authentication and with what logs. Steinman’s level about proof of who reached a controller and what modified solely works if these logs exist.
5. Add temperature monitoring that doesn’t report by means of the controller. A separate sensor with its personal alert path catches a controller that’s compromised or misreporting. That’s our suggestion fairly than an official one, and it follows from Claroty’s demonstration, as Infosecurity Journal described it, {that a} compromised AK-SM 800A might minimize cooling whereas exhibiting false temperatures.
The Query That Outlasts the Investigation
Investigators will in all probability identify an entry route, and a CVE quantity might comply with. The tougher query is the one the retailers and the producer are already answering in a different way: who was liable for maintaining that controller present and its login closed? Operators that may reply that for each chilly room they run will probably be higher positioned when the subsequent advisory lands, and those who can not are leaving the reply to whoever scans the web first.