How content-addressed storage, immutable state, and specific lifecycle occasions could make digital credentials simpler to confirm
Digital Credentials Have a Verification Drawback
Digital certificates are simple to distribute. Verification turns into more durable as soon as a doc leaves the system that issued it. A verifier could obtain a PDF with no direct solution to decide whether or not it’s the precise file initially issued, whether or not the metadata related to it has modified, or whether or not the supposed recipient ever accepted the credential.
One solution to tackle this downside is to separate the credential into layers. Content material-addressed storage can establish the precise doc, structured metadata can describe the credential, an immutable state layer can protect a sturdy reference, and specific lifecycle occasions can file issuance and acceptance. D-Certify, a credential-verification undertaking developed by software program engineer Kyrylo Sotnykov, offers a sensible instance of this design sample.
Begin With Content material Addressing
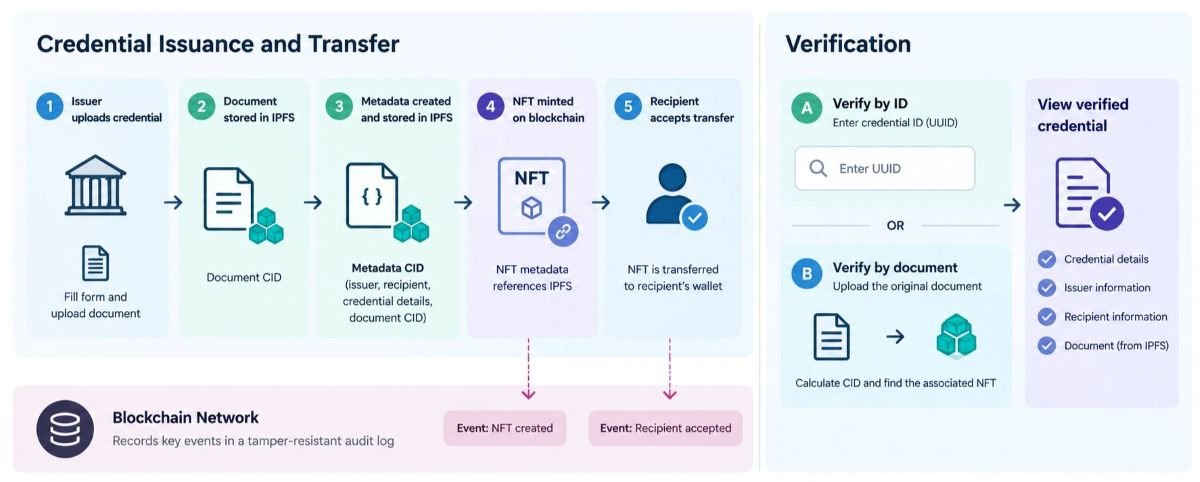
Within the D-Certify workflow, an issuer completes a credential kind and uploads the certificates or supporting doc. The file is saved in IPFS, which returns a content material identifier, or CID. As a result of the CID is derived from the file content material, altering the file produces a distinct identifier.
The system then creates JSON metadata containing issuer, recipient, and certificates info along with the doc CID. That metadata can also be saved in IPFS. The result’s a content-addressed chain by which structured metadata factors to the precise doc that existed at issuance time.
Use the Ledger as a Sturdy Reference
A reference to the IPFS metadata is written into the metadata discipline of a Hedera NFT when the token is minted. The NFT just isn’t the certificates itself. It acts as an on-chain reference to metadata that, in flip, factors to the unique doc. This retains doc storage and ledger state distinct reasonably than treating a distributed ledger as a general-purpose doc database.
Determine 1. A layered credential workflow separating doc content material, metadata, immutable state, recipient acceptance, and verification.
Make Recipient Acceptance Express
At creation, the NFT initially stays within the issuer’s account. The supposed recipient should settle for the switch earlier than the token strikes to the recipient’s account. That distinction issues as a result of issuance and acceptance are completely different lifecycle occasions: a credential will be created earlier than the recipient confirms possession of it.
The structure additionally data essential lifecycle occasions by Hedera Consensus Service. Occasions are written when the NFT is created and when the recipient confirms acceptance, offering an ordered audit path alongside token possession.
Verification Ought to Reconstruct the Credential
Verification can start in two methods. If the verifier has the credential’s inner UUID, the system can find the related file immediately. If the verifier solely has the doc, the file will be uploaded and its CID calculated. An altered file produces a distinct CID, so the uploaded content material itself turns into a part of the verification path.
Utilizing the calculated CID, the system can find the related NFT, resolve its metadata reference, retrieve the credential metadata, and show the outcome. The target is to not decide whether or not a certificates appears to be like genuine. It’s to find out whether or not the precise uploaded content material will be linked again to the credential reference created at issuance.
What This Structure Does – and Does Not – Show
Content material integrity just isn’t the identical as issuer belief. A CID can present {that a} file matches referenced content material, however a verifier nonetheless wants confidence that the issuer is professional and licensed to difficulty that credential. NFT possession likewise shouldn’t be handled as proof of each declare contained within the certificates; it’s one observable state in a bigger verification chain.
Privateness requires related care. Maintaining the certificates itself outdoors the ledger doesn’t mechanically make the system personal. Metadata saved in IPFS should still be retrievable by anybody who obtains its CID, relying on system configuration and the knowledge included. Information minimization, entry controls, and cautious metadata design stay essential.
Actual-World Testing Exposes Operational Gaps
Early deployments are helpful as a result of they expose issues that structure diagrams typically miss. Sotnykov’s D-Certify implementation has been utilized in restricted hackathon workflows, together with Iris Hacks IV and the International Builders Hackathon, to difficulty verifiable credentials to chose members or winners. These deployments stay small in scale, however they train the complete lifecycle: issuer enter, doc storage, metadata creation, token minting, recipient acceptance, audit occasions, and later verification.
That end-to-end use highlights sensible questions similar to tips on how to deal with incorrect uploads, reissuance, unavailable IPFS content material, compromised issuer entry, revocation, and consumer confusion round token acceptance. In manufacturing methods, these operational particulars typically matter as a lot because the ledger expertise itself.
A Sample That Extends Past Certificates
The broader lesson just isn’t merely to “put credentials on a blockchain.” It’s to construct a series of independently checkable references. Content material addressing identifies the precise artifact. Structured metadata connects it to issuer and recipient info. An immutable state layer preserves the reference and possession state. Separate occasion logs protect essential lifecycle actions.
The identical separation of issues can apply past certificates. Compliance data, software program attestations, coaching credentials, and different digital artifacts could profit from architectures by which integrity, metadata, possession, and lifecycle historical past will be verified independently. The worth comes from making state reproducible and limits specific, not from utilizing a ledger for each a part of the system.
Classes for Platform Groups
For platform and infrastructure groups, a number of design ideas emerge. Giant artifacts and sturdy state can reside in several layers. Verification is stronger when it may be reproduced from the artifact a consumer truly possesses. State transitions similar to issuance and acceptance needs to be specific and observable. Audit logs and software state remedy completely different issues and shouldn’t be handled as interchangeable.
Clear failure modes are equally essential. A verifier ought to be capable of distinguish between a CID that doesn’t resolve, a doc with no related token, unavailable metadata, and a credential that has not but been accepted. Reliable verification relies upon not solely on proving success, but in addition on making failure comprehensible.
How content-addressed storage, immutable state, and specific lifecycle occasions could make digital credentials simpler to confirm
Digital Credentials Have a Verification Drawback
Digital certificates are simple to distribute. Verification turns into more durable as soon as a doc leaves the system that issued it. A verifier could obtain a PDF with no direct solution to decide whether or not it’s the precise file initially issued, whether or not the metadata related to it has modified, or whether or not the supposed recipient ever accepted the credential.
One solution to tackle this downside is to separate the credential into layers. Content material-addressed storage can establish the precise doc, structured metadata can describe the credential, an immutable state layer can protect a sturdy reference, and specific lifecycle occasions can file issuance and acceptance. D-Certify, a credential-verification undertaking developed by software program engineer Kyrylo Sotnykov, offers a sensible instance of this design sample.
Begin With Content material Addressing
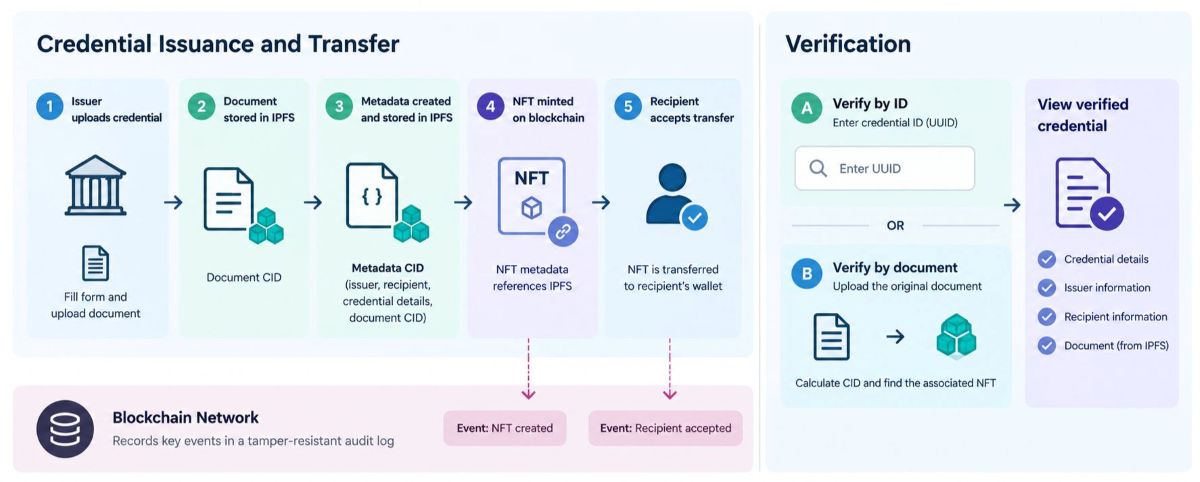
Within the D-Certify workflow, an issuer completes a credential kind and uploads the certificates or supporting doc. The file is saved in IPFS, which returns a content material identifier, or CID. As a result of the CID is derived from the file content material, altering the file produces a distinct identifier.
The system then creates JSON metadata containing issuer, recipient, and certificates info along with the doc CID. That metadata can also be saved in IPFS. The result’s a content-addressed chain by which structured metadata factors to the precise doc that existed at issuance time.
Use the Ledger as a Sturdy Reference
A reference to the IPFS metadata is written into the metadata discipline of a Hedera NFT when the token is minted. The NFT just isn’t the certificates itself. It acts as an on-chain reference to metadata that, in flip, factors to the unique doc. This retains doc storage and ledger state distinct reasonably than treating a distributed ledger as a general-purpose doc database.
Determine 1. A layered credential workflow separating doc content material, metadata, immutable state, recipient acceptance, and verification.
Make Recipient Acceptance Express
At creation, the NFT initially stays within the issuer’s account. The supposed recipient should settle for the switch earlier than the token strikes to the recipient’s account. That distinction issues as a result of issuance and acceptance are completely different lifecycle occasions: a credential will be created earlier than the recipient confirms possession of it.
The structure additionally data essential lifecycle occasions by Hedera Consensus Service. Occasions are written when the NFT is created and when the recipient confirms acceptance, offering an ordered audit path alongside token possession.
Verification Ought to Reconstruct the Credential
Verification can start in two methods. If the verifier has the credential’s inner UUID, the system can find the related file immediately. If the verifier solely has the doc, the file will be uploaded and its CID calculated. An altered file produces a distinct CID, so the uploaded content material itself turns into a part of the verification path.
Utilizing the calculated CID, the system can find the related NFT, resolve its metadata reference, retrieve the credential metadata, and show the outcome. The target is to not decide whether or not a certificates appears to be like genuine. It’s to find out whether or not the precise uploaded content material will be linked again to the credential reference created at issuance.
What This Structure Does – and Does Not – Show
Content material integrity just isn’t the identical as issuer belief. A CID can present {that a} file matches referenced content material, however a verifier nonetheless wants confidence that the issuer is professional and licensed to difficulty that credential. NFT possession likewise shouldn’t be handled as proof of each declare contained within the certificates; it’s one observable state in a bigger verification chain.
Privateness requires related care. Maintaining the certificates itself outdoors the ledger doesn’t mechanically make the system personal. Metadata saved in IPFS should still be retrievable by anybody who obtains its CID, relying on system configuration and the knowledge included. Information minimization, entry controls, and cautious metadata design stay essential.
Actual-World Testing Exposes Operational Gaps
Early deployments are helpful as a result of they expose issues that structure diagrams typically miss. Sotnykov’s D-Certify implementation has been utilized in restricted hackathon workflows, together with Iris Hacks IV and the International Builders Hackathon, to difficulty verifiable credentials to chose members or winners. These deployments stay small in scale, however they train the complete lifecycle: issuer enter, doc storage, metadata creation, token minting, recipient acceptance, audit occasions, and later verification.
That end-to-end use highlights sensible questions similar to tips on how to deal with incorrect uploads, reissuance, unavailable IPFS content material, compromised issuer entry, revocation, and consumer confusion round token acceptance. In manufacturing methods, these operational particulars typically matter as a lot because the ledger expertise itself.
A Sample That Extends Past Certificates
The broader lesson just isn’t merely to “put credentials on a blockchain.” It’s to construct a series of independently checkable references. Content material addressing identifies the precise artifact. Structured metadata connects it to issuer and recipient info. An immutable state layer preserves the reference and possession state. Separate occasion logs protect essential lifecycle actions.
The identical separation of issues can apply past certificates. Compliance data, software program attestations, coaching credentials, and different digital artifacts could profit from architectures by which integrity, metadata, possession, and lifecycle historical past will be verified independently. The worth comes from making state reproducible and limits specific, not from utilizing a ledger for each a part of the system.
Classes for Platform Groups
For platform and infrastructure groups, a number of design ideas emerge. Giant artifacts and sturdy state can reside in several layers. Verification is stronger when it may be reproduced from the artifact a consumer truly possesses. State transitions similar to issuance and acceptance needs to be specific and observable. Audit logs and software state remedy completely different issues and shouldn’t be handled as interchangeable.
Clear failure modes are equally essential. A verifier ought to be capable of distinguish between a CID that doesn’t resolve, a doc with no related token, unavailable metadata, and a credential that has not but been accepted. Reliable verification relies upon not solely on proving success, but in addition on making failure comprehensible.