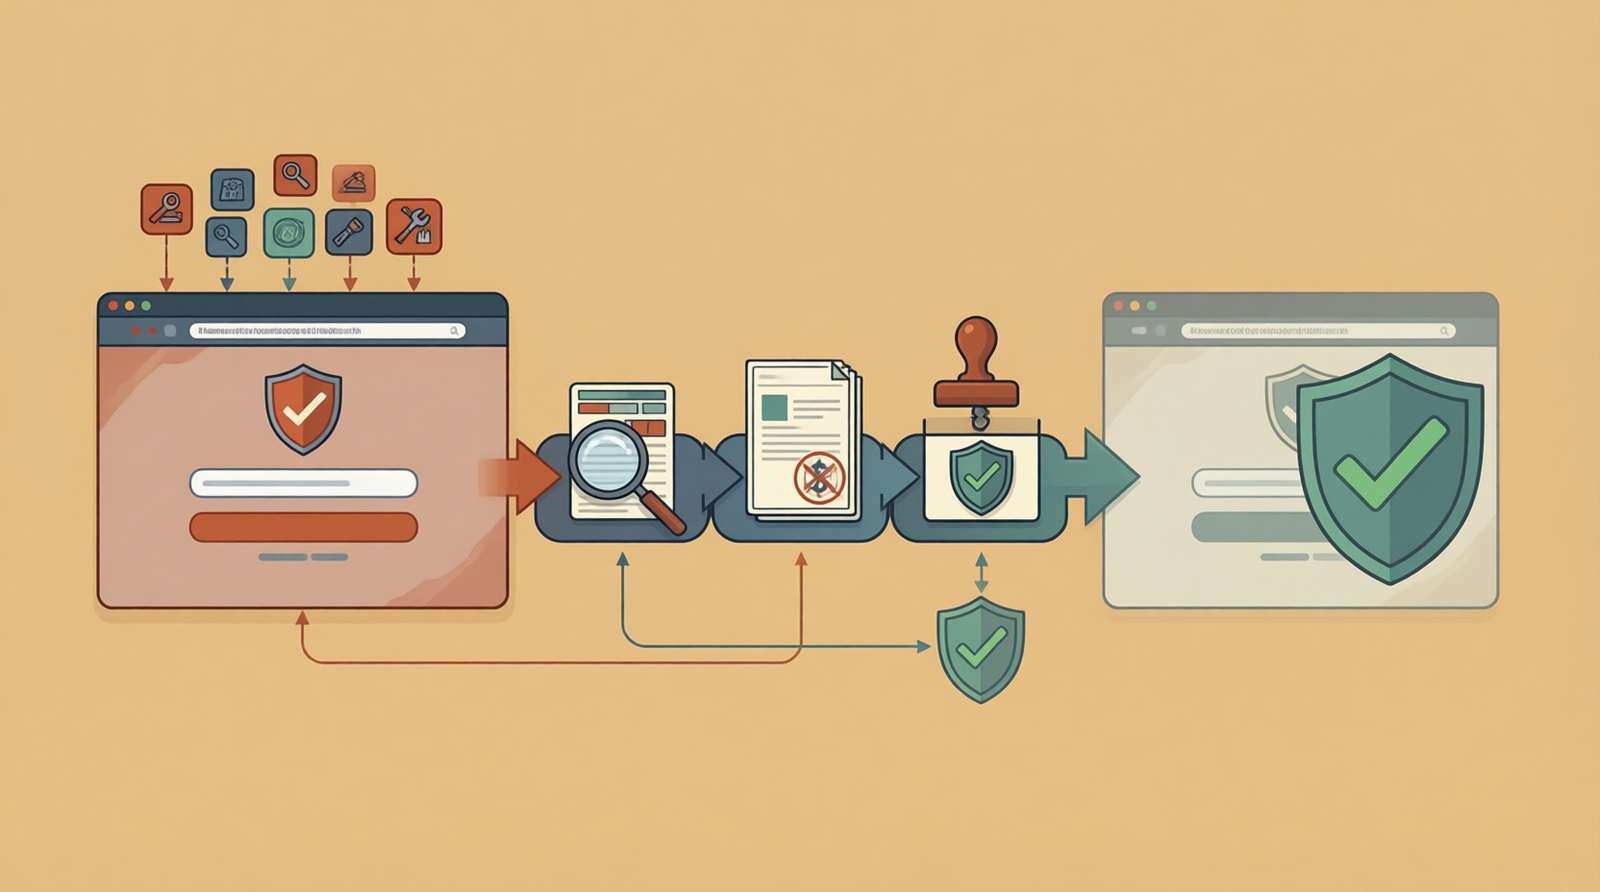
Model safety means various things to totally different groups. A authorized group might must take away counterfeit market listings. A safety group might must discover a pretend login web page, a fraudulent social profile, or a rogue software impersonating the corporate. These issues overlap, however they don’t require equivalent proof or enforcement workflows.
Select a model safety software by following a phishing or impersonation case from detection by verified elimination. Examine supported channels, retained proof, analyst validation, approval necessities, and enforcement accountability. To your safety group, the deciding issue is whether or not the supplier helps the response workflow you want, not merely what number of suspicious property it finds.
This comparability focuses on phishing and impersonation that create safety threat for purchasers, workers, and companions. Examine Level is related when model threats want to attach with a broader exterior publicity program. Netcraft is a powerful shortlist entry for on-line risk detection and takedown workflows. ZeroFox, Recorded Future, BrandShield, and UpGuard present different helpful approaches to digital threat and model abuse.
A very powerful consequence is what occurs after a suspicious asset is discovered: who validates it, who is allowed to behave, and the way the group confirms the risk has been disrupted.
We chosen merchandise with a documented function in detecting, investigating, or responding to phishing and impersonation. Netcraft begins the disruption-focused comparability, adopted by Examine Level for integration with broader exterior threat. This scope excludes a complete rating of trademark, piracy, counterfeit, and domain-registration companies.
Suggestions use official product pages and documentation. No hands-on efficiency benchmark was carried out. This text was ready for a Examine Level content material mission; product numbers assist navigation and don’t signify unbiased scores.
Examine the response mannequin
Examine every software in opposition to the channels your group should defend and the work required after detection. Proof assessment, approval, enforcement, and verified elimination belong in the identical analysis. A supplier that submits a request has accomplished a special step from one which confirms the abusive useful resource is gone.
Netcraft’s 2026 platform comparability covers options, integrations, and efficiency. The desk beneath retains these questions tied to the response mannequin of every shortlisted software. Its affirmation column describes what to verify throughout an analysis, quite than assigning an untested efficiency rating or assuming that each product consists of managed elimination.
| Software | Helpful beginning requirement | What to substantiate |
|---|---|---|
| Netcraft | On-line risk detection and disruption | Proof, enforcement workflow, reporting, and proof confirming elimination |
| Examine Level | Model threats linked to exterior intelligence and publicity | Supported channels, validation, takedown scope, and proof confirming elimination |
| ZeroFox | Digital threat throughout impersonation channels | Channel protection, disruption service particulars, and proof confirming elimination |
| Recorded Future | Digital threat linked to intelligence workflows | Included detection and takedown capabilities, and proof confirming elimination |
| BrandShield | Model abuse throughout web sites, social, adverts, and marketplaces | Cybersecurity versus intellectual-property necessities, and proof confirming elimination |
| UpGuard Breach Danger | Model threats inside broader exterior threat operations | Supported circumstances, remediation accountability, and proof confirming elimination |
Consider the info and AI behind every case
Consider the info your group receives with every detection, not simply the alert depend. Examine monitored channels, the reason for flagging an asset, case proof fields, and integration choices. Preserve the elimination consequence separate from the request standing so your data present what was truly disrupted.
Map protection to the property it is advisable examine: domains, web sites, social profiles, functions, adverts, or market listings. For every channel, have the supplier reveal what reaches the case report and what an analyst should accumulate manually. A suspicious URL with out the noticed habits leaves your group repeating the investigation. Protect the supply and statement time with the proof so a reviewer can perceive what was seen when the discovering was raised.
If a vendor describes its detection as AI-driven, use an ambiguous case to look at the reason. Require the assessment to indicate why the asset was flagged and which observations help the choice. The same identify alone shouldn’t be handled as proof of credential theft. Examine that consequence with a recognized licensed accomplice to see how your approved-asset checklist impacts assessment and whether or not an analyst can right the case earlier than enforcement begins.
For the case proof schema, require separate fields for the asset, affected model or particular person, noticed habits, supply proof, assessment resolution, approval, response standing, and elimination verify. Preserve the unique proof obtainable when a case modifications palms. Your knowledge governance course of also needs to assign an proprietor to the accepted checklist of domains, accounts, functions, and companions. In any other case, a reputable launch can arrive within the investigation queue with out anybody understanding who licensed it.
Take a look at any proposed API or export with an entire case, together with a later standing change. Examine whether or not your present case system receives the proof and approval historical past, or solely an alert and a hyperlink again to the seller dashboard. Use distinct data for a submitted elimination request and the next verification. If the asset stays reachable, the combination ought to protect that discovering quite than treating submission as closure. These are analysis necessities, not assumed capabilities of each software beneath.
1. Netcraft
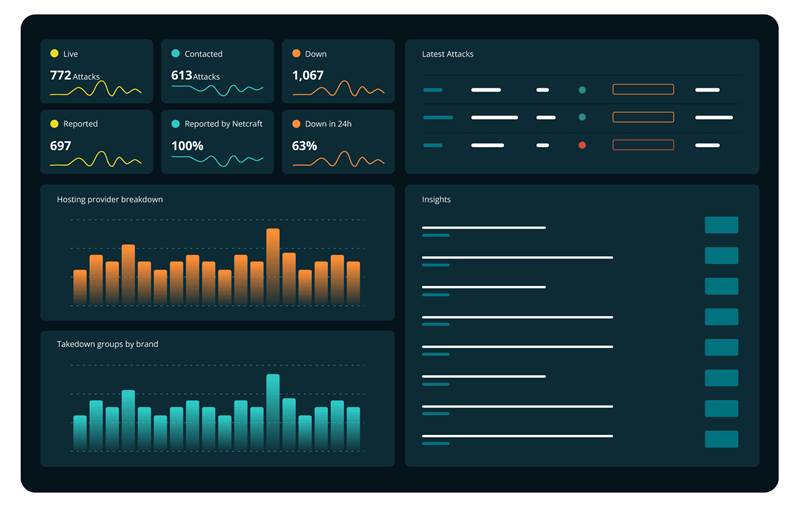
Vendor interface illustration. Netcraft’s stylized threat-response dashboard; displayed figures are illustrative. Supply.
Netcraft is a related shortlist entry when the core want is detecting and disrupting on-line threats that impersonate the group. Its platform describes risk intelligence and reporting workflows, together with dashboards that monitor exercise and outcomes. This makes it helpful to evaluate when the safety group wants a transparent operational view of phishing and associated abuse. Official product info.
The analysis ought to observe a consultant incident from discovery to proof assessment, enforcement, and closure. Verify how the supplier handles circumstances that rely upon a third-party internet hosting supplier, registrar, social platform, or different middleman. Additionally outline what the reported consequence means: an abuse report submitted, a useful resource eliminated, or a risk now not reachable. These distinctions are extra informative than an unqualified takedown-speed declare.
2. Examine Level
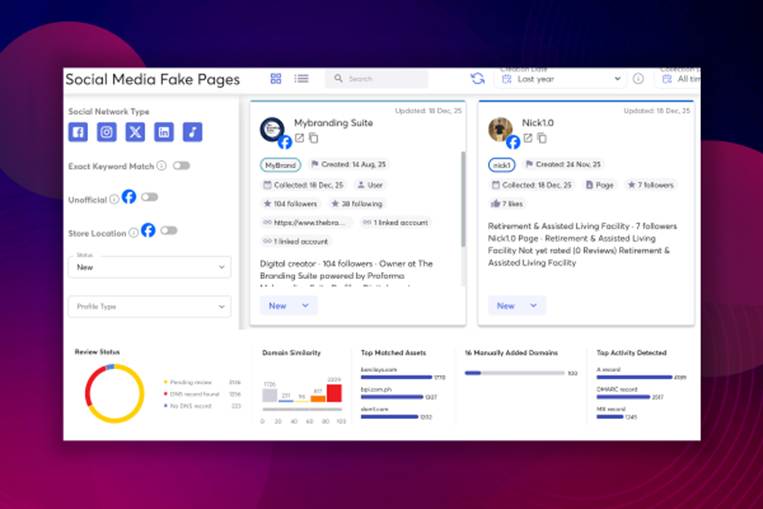
Revealed product interface. Examine Level’s printed model safety view for investigating impersonating pages. Supply.
Examine Level’s risk intelligence supplies embody model abuse as a part of exterior threat administration. Its remediation supplies describe takedown-related responses to exterior threats resembling phishing pages, impersonation, and rogue functions. This can be a helpful match when the safety group needs model threats thought of alongside uncovered property, credentials, and different exterior indicators. Official product info.
The sensible benefit is context. A suspicious area could also be extra pressing when it’s linked to a wider marketing campaign or one other publicity affecting the group. Scope the Examine Level exterior risk intelligence and remediation capabilities required for this system. Verify supported channels, what analysts validate, what the service does after approval, and the way completion is reported. A detection will not be the identical as a accomplished takedown.
3. ZeroFox
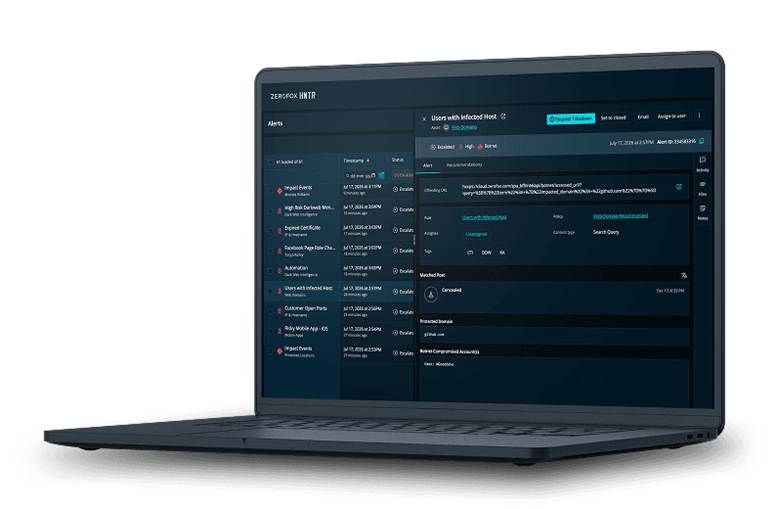
Revealed interface composite. ZeroFox’s printed interface within the vendor’s authentic gadget body. Supply.
ZeroFox’s present platform combines exterior intelligence and digital threat capabilities with disruption. Its supplies deal with model and impersonation issues alongside different exterior risk areas. It’s related when the group wants a broader exterior threat operation that features customer-facing and executive-related threats. Official product info.
Begin by naming the channels the enterprise truly makes use of and the types of impersonation that trigger hurt. Then verify detection and response protection for these particular circumstances. A broad digital threat platform might be helpful throughout a number of groups, however tasks ought to stay clear. Safety, communications, fraud, and authorized groups might have totally different proof and approval paths earlier than a supplier requests elimination of an asset.
4. Recorded Future Digital Danger Safety
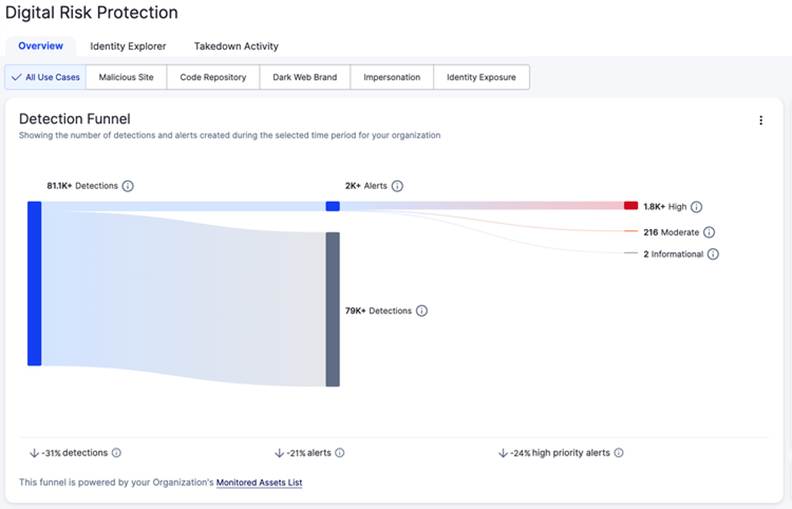
Revealed product interface. Recorded Future’s printed digital threat detection funnel. Supply.
Recorded Future’s Digital Danger Safety providing connects exterior detections with investigation and takedown-related workflows. Its product supplies present a detection funnel and operational reporting. It’s a related choice when a group needs model abuse and different exterior dangers to sit down alongside a longtime intelligence program. Official product info.
The helpful comparability is how a case strikes by that funnel. Examine the proof, the rationale for prioritization, and the stage at which a human evaluations or approves the motion. Verify the modules, channels, and enforcement scope included within the proposed buy. A digital threat detection and a technical risk intelligence consequence might help the identical investigation, however they need to retain their supply context and distinct response necessities.
5. BrandShield
Vendor illustration. BrandShield’s printed protection illustration. This depicts monitoring scope quite than a stay product interface. Supply.
BrandShield is related when the group’s model abuse downside spans web sites, domains, social media, paid promoting, and marketplaces. Its supplies cowl a broader model safety scope than a phishing-only product, making it value contemplating when cybersecurity and intellectual-property issues share an working group. Official product info.
That breadth ought to be matched to the precise requirement. A pretend help profile and a counterfeit product itemizing require totally different proof and should contain totally different enforcement processes. Outline each the safety and authorized use circumstances earlier than evaluating protection or value. The strongest match is a company that may coordinate these tasks and wishes a supplier to help the related channels, quite than assuming each brand-related incident follows the identical takedown process.
6. UpGuard Breach Danger
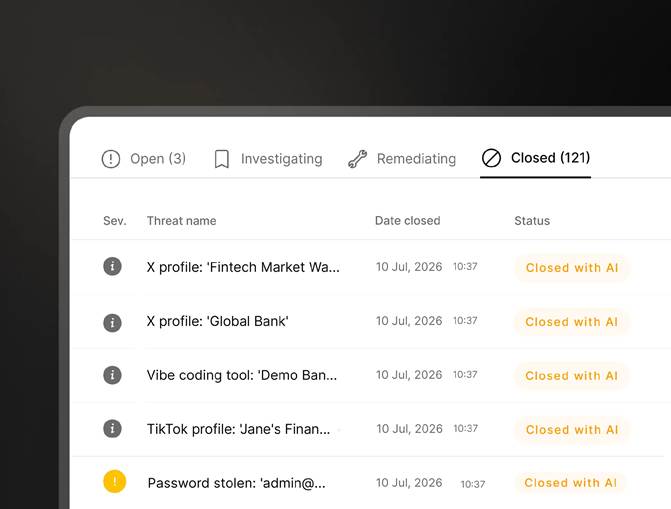
Revealed product interface. UpGuard’s printed model risk case checklist. Supply.
UpGuard’s present Breach Danger providing consists of model threats inside a wider exterior threat view that additionally covers knowledge leaks and assault floor issues. It’s related when the group needs to analyze impersonation alongside different indicators that the group or its prospects could also be uncovered. Official product info.
Use a sensible case to look at how the platform presents the suspicious asset, supporting proof, and advisable subsequent motion. Verify which response capabilities are included and which stay the shopper’s accountability. That is particularly necessary when evaluating a broader exterior threat product with a service constructed round managed enforcement. A shared dashboard can enhance triage, whereas the precise authority and mechanism for eradicating abusive content material nonetheless should be established.
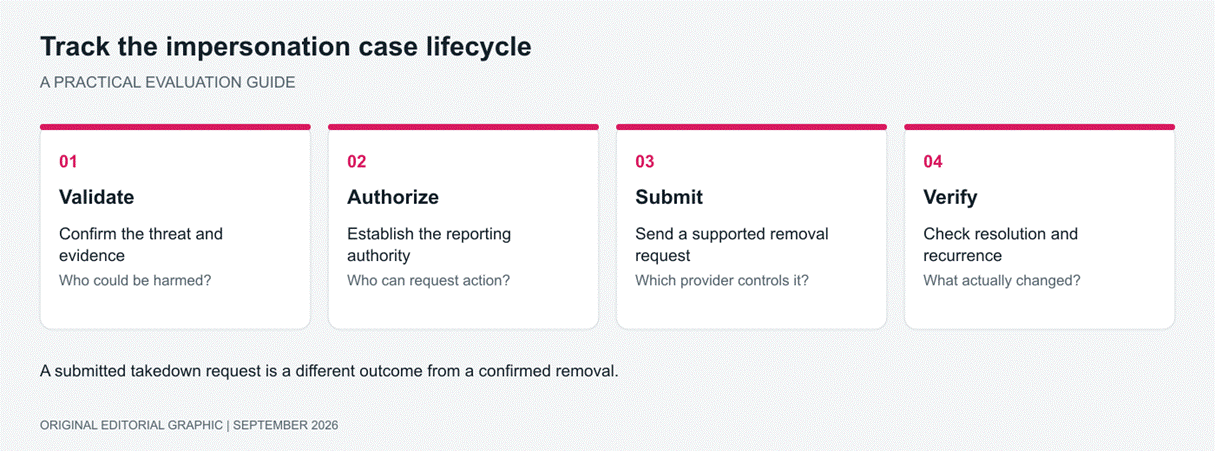
Unique editorial graphic. Observe verified elimination individually from a submitted request.
What makes an impersonation discovering helpful?
A helpful case offers the group sufficient proof to tell apart dangerous impersonation from a reputable accomplice, commentary, or unrelated use of an analogous identify. It ought to establish the asset, the noticed habits, the affected model or particular person, and the rationale the case is actionable. Proof ought to be retained in a type the accountable group can assessment.
The excellence issues operationally. A lookalike area with no lively content material might deserve monitoring, whereas a web page amassing credentials below the corporate’s identification might require pressing motion. A supplier ought to assist the group prioritize these variations as an alternative of presenting each match as equally extreme.
Additionally account for reputable property. Keep an accepted checklist of official domains, social accounts, functions, and licensed companions, with a course of for updating it. This offers the supplier helpful context and reduces pointless investigation when the enterprise launches one thing new.
Take a look at the complete case lifecycle
Use a managed train or historic circumstances the group is allowed to share. Embrace a number of related channels and no less than one ambiguous case. Ask every supplier to clarify what it could detect, what proof it could accumulate, and which response path it could use.
Examine the transitions between detected, validated, submitted for motion, and resolved. For a takedown request, set up who approves the request and which exterior occasion in the end controls elimination. A supplier can coordinate and pursue enforcement with out controlling each middleman’s resolution or response time.
After closure, study how the group verifies the end result and handles recurrence. Eradicating one web page might not take away the broader marketing campaign. The case report ought to protect sufficient context to attach associated property and clarify what was truly disrupted.
Examine pricing in opposition to the circumstances you count on
Request a scope that names the protected manufacturers, domains, individuals, areas, and channels. Ask how monitoring, investigations, takedown makes an attempt, analyst help, and escalations are counted. This creates a helpful business comparability with out counting on unsupported public value estimates.
Additionally outline inside workload. A decrease subscription value might be much less engaging if the shopper should validate each case, accumulate proof, and negotiate each escalation. Conversely, a group with established response processes might favor a product that integrates with these processes quite than a broad managed service.
Begin with Examine Level when impersonation wants to attach with a wider exterior intelligence and publicity program. Examine Netcraft carefully for on-line risk disruption, and embody ZeroFox or Recorded Future for broader digital threat operations. BrandShield is related when the scope additionally consists of model abuse throughout business channels. UpGuard is helpful to check when exterior threat consolidation is a central requirement.
The only option is the one which turns a related detection right into a well-supported, licensed, and verifiable response. Counting suspicious URLs is a beginning metric; lowering the hurt attributable to impersonation is the rationale for this system.
FAQ
Examine model safety instruments utilizing proof from the channels your organization wants to guard. Revealed takedown charges can inform the dialogue, however your analysis ought to observe the case by validation, approval, and confirmed elimination. Pricing ought to replicate each the supplier’s work and the investigations your group retains.
Which model safety software has a documented takedown price for impersonation?
Bitsight’s 2026 model safety and impersonation monitoring comparability studies an 85% takedown price and describes impersonation detection. This can be a vendor-reported determine, not a consequence from this text’s testing. Consider the six shortlisted instruments utilizing their very own verified elimination proof. Earlier than evaluating percentages, set up which circumstances enter the calculation, the measurement interval, and what counts as a profitable elimination.
How ought to I evaluate model safety instruments for phishing and impersonation?
Examine detection channels, proof high quality, human approval, takedown workflow, and verified elimination metrics. Run the identical licensed historic circumstances or managed train by every analysis. Embrace an ambiguous discovering so you’ll be able to examine how the supplier distinguishes dangerous impersonation from reputable exercise. Examine whether or not proof and standing modifications attain your group’s present case system with out dropping supply context.
What ought to I ask distributors about model safety pricing?
Request scope by manufacturers, domains, individuals, areas, and channels. Ask how monitoring, investigations, takedown makes an attempt, analyst help, and escalations are billed. Set up which duties stay together with your group, particularly proof assortment, validation, approvals, and follow-up with intermediaries. Examine these tasks alongside the subscription value so a inexpensive supply doesn’t conceal considerably extra inside work.
Make verified elimination a part of case closure
Require a elimination verify earlier than your group closes an impersonation case. Preserve the approval, submitted request, and noticed consequence as separate data tied to the affected asset. That distinction prevents a accomplished administrative step from being mistaken for proof {that a} phishing web page is now not reachable.
A case marked resolved can nonetheless depart the underlying abuse unaddressed. Through the analysis, evaluate the supplier’s closure report with the proof your analyst can assessment for a similar asset. File when the end result was checked and what remained accessible. If one other associated web page seems, maintain its connection to the sooner case seen quite than dropping the marketing campaign context in a brand new alert. Earlier than accepting an integration, verify that these particulars survive the switch into your individual case system.