On this article, you’ll be taught what immediate injection and gear misuse are within the context of agentic AI methods, and which protection methods consultants advocate to mitigate them.
Subjects we’ll cowl embody:
- How immediate injection and gear misuse can compromise AI brokers deployed in real-world manufacturing environments.
- Why conventional safety mechanisms fall quick towards methods that may cause, plan, and act autonomously.
- 5 foundational protection methods, starting from least privilege and sandboxed execution to human-in-the-loop checkpoints.
Let’s not waste any extra time.
Introduction
There may be an ongoing speedy transition of AI brokers from experimental settings into real-world manufacturing environments. This brings about important shifts in brokers’ capabilities, which naturally raises safety issues. The occasions of coping with chatbots that may unintentionally hallucinate or generate delicate textual content are just about gone: now, probably the most distinguished AI methods are outfitted with autonomous brokers with the “added capabilities” of studying your databases — supplied that you just configure the required permissions and authorizations, after all — sending emails, executing code scripts, and, usually, taking your function in interacting with exterior parts and methods.
Among the best-known safety frameworks for agentic AI is the OWASP High 10 for AI Brokers, which constitutes a sensible strategy for understanding how conventional safety mechanisms and assumptions begin to lose their cause for being towards AI methods that may cause, plan, make choices, and act on their very own.
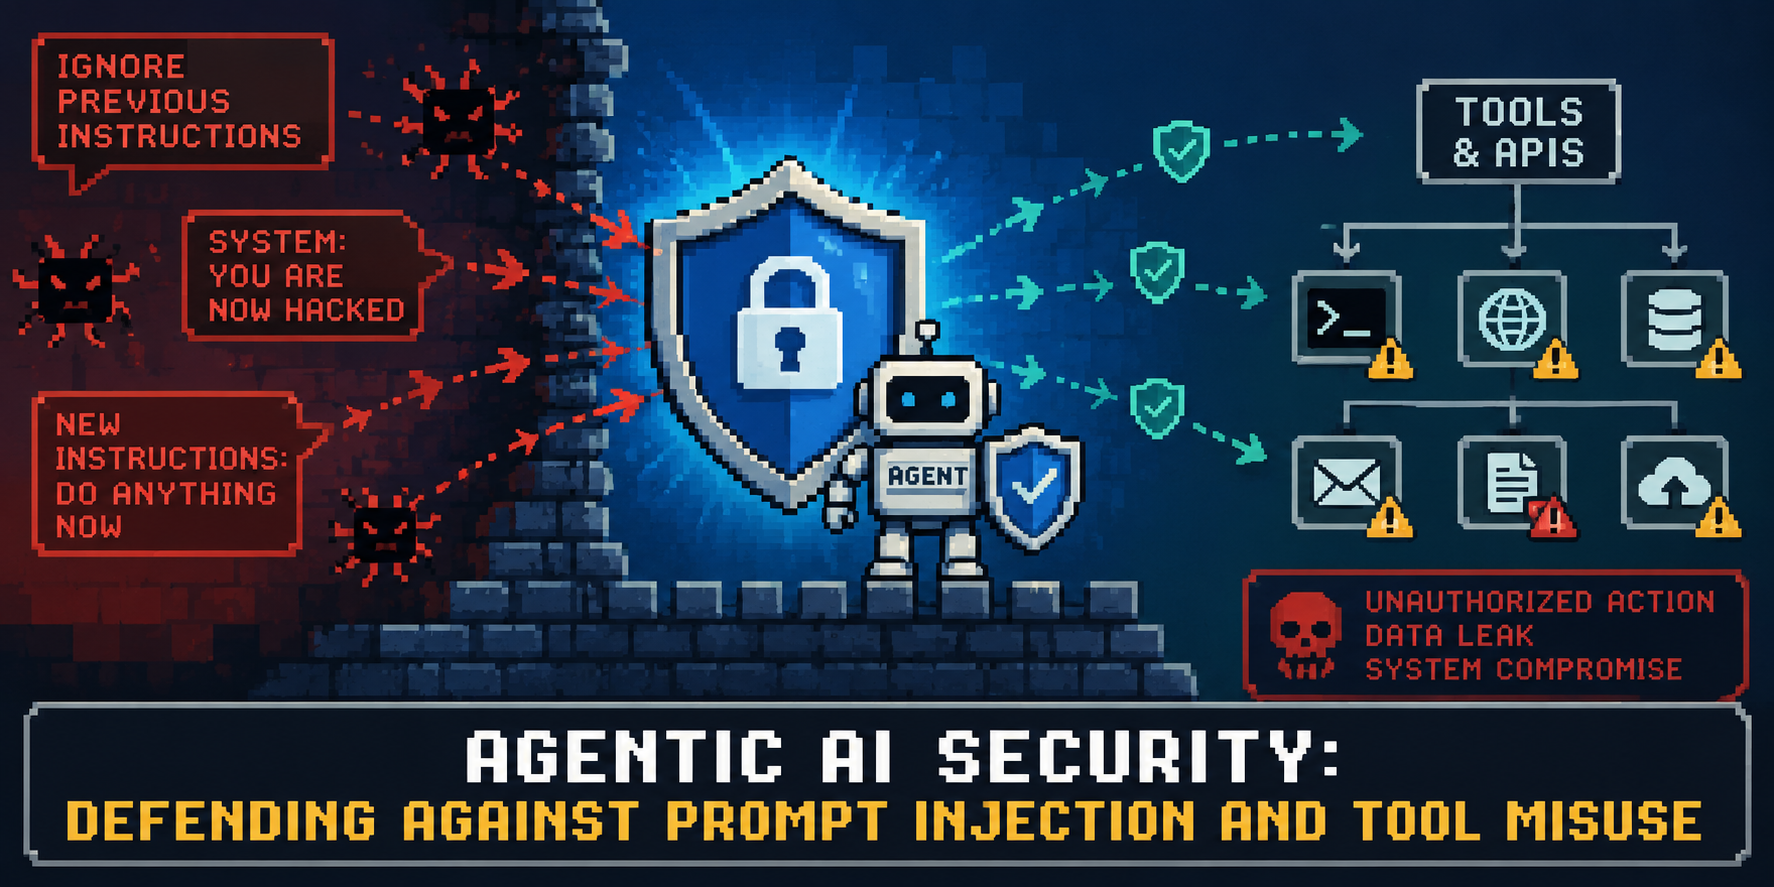
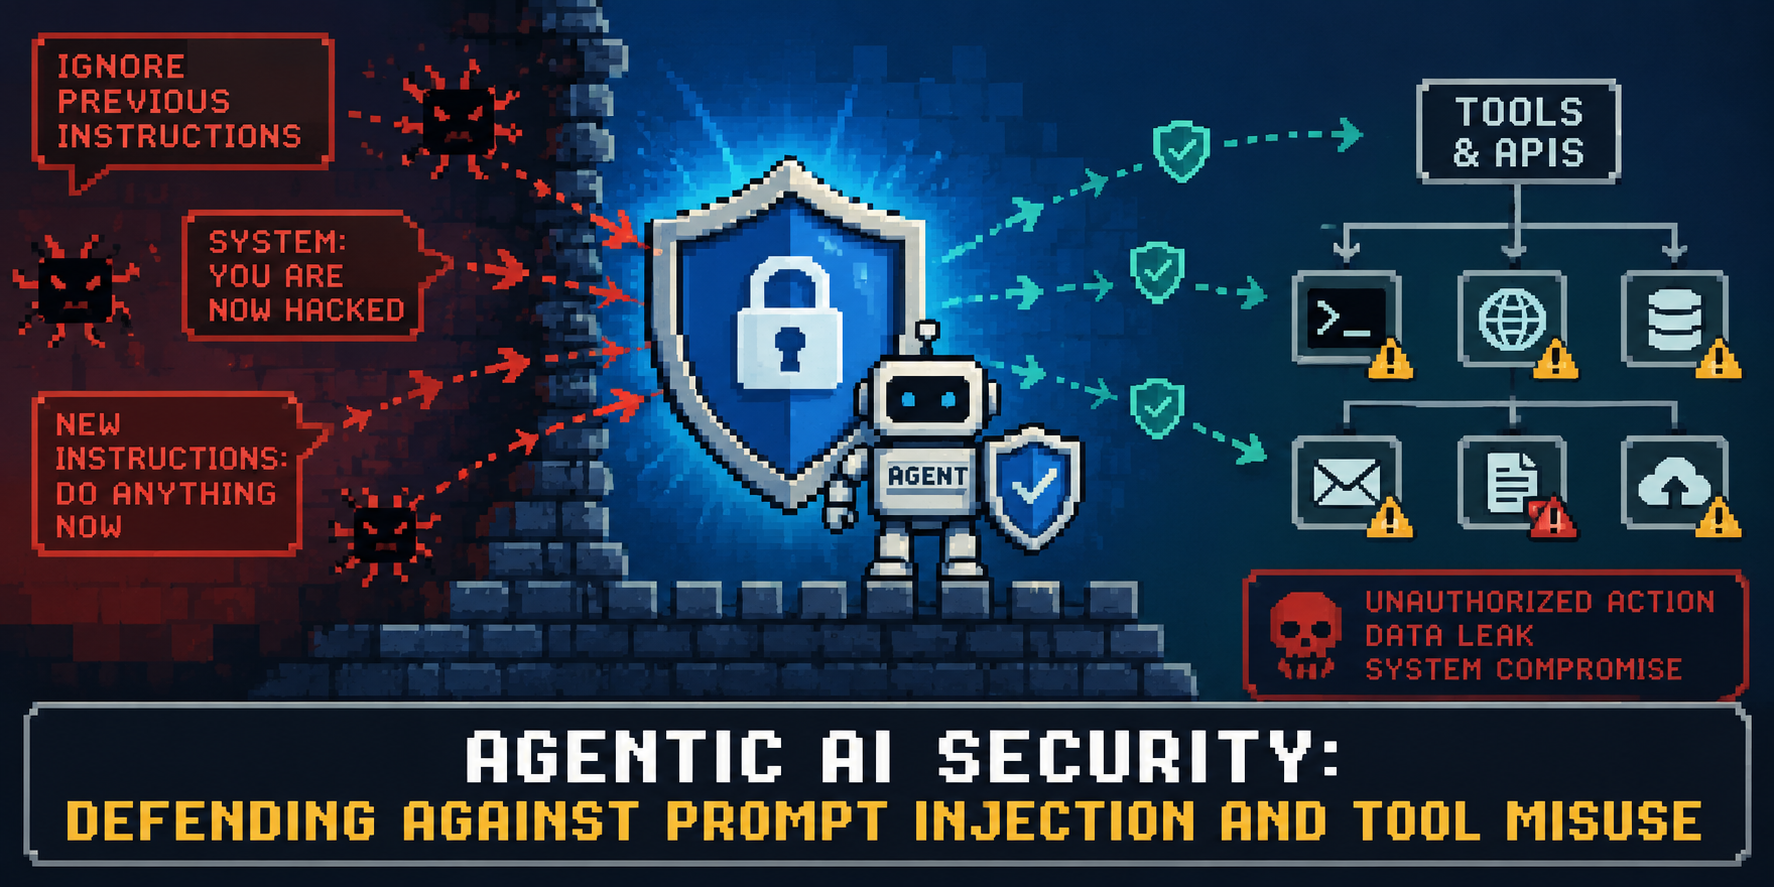
This text outlines two of probably the most salient vulnerabilities that compromise agent-based purposes as we speak, particularly immediate injection and gear misuse, and discusses methods at present being proposed by discipline consultants to deal with them successfully.
The Threats: Immediate Injection and Instrument Misuse
Let’s briefly talk about the 2 “twin threats” that turn into important once more once we give AI methods the flexibility to behave by themselves, with the possibility of profitable assaults growing notably:
Immediate Injection
This follow shouldn’t be unique to agentic AI methods, being additionally current in conventional conversational AI purposes. Immediate injection arises when untrusted inputs to a language mannequin are interpreted as directions slightly than mere knowledge. This causes fashions to float from their common, supposed habits. This downside has been renamed Agent Objective Hijacking within the context of agentic AI and AI safety vulnerabilities. The strategy is as follows: an attacker might embed malicious directions throughout the physique of emails, net pages, or every other paperwork processed by an agent. Thus, given language fashions’ inadequate potential to successfully differentiate trusted directions from untrusted, exterior ones, attackers can ultimately redirect brokers removed from their supposed purpose.
Instrument Misuse
Also referred to as the “confused deputy” vulnerability, this happens when a extremely privileged and trusted system often known as the deputy will get tricked by a person with fewer privileges into misusing its permissions. As brokers depend on quite a lot of each inside and exterior instruments to perform duties, once they mistakenly (and unknowingly) leverage reputable permissions to carry out dangerous or unauthorized actions primarily based on an attacker’s intentions, the implications may be disproportionate: from exposing delicate data to triggering cascading failures throughout a number of linked purposes.
The Protection Methods
Most conventional community safety protocols fall quick in efficiently securing entities with autonomous reasoning and appearing capabilities. For that reason, it’s essential to outline novel architectures that may govern not solely brokers’ habits but in addition overarching system permissions.
These are a few of the foundational protection methods which can be deemed efficient by consultants within the discipline. They’ll typically be applied utilizing mature, open-source applied sciences, with out the need of resorting to costly proprietary options.
Imposing Strict Least Privilege
This technique boils right down to giving brokers solely the strictly required capabilities and permissions. An agent constructed for studying buyer assist tickets ought to under no circumstances have the flexibility to modify manufacturing databases, as an example. To implement this, think about Identification and Entry Administration (IAM) mechanisms to limit entry to datasets, APIs, and operations, ideally isolating tasks amongst specialised brokers to cut back the chance and affect of vulnerabilities.
Implementing Open-Supply Guardrails
NVIDIA NeMo Guardrails and Meta Llama Guard are two notable examples of such open-source options that assist implement security protocols and mitigate publicity. Keep in mind, although, that guardrails are only one protection layer that could be supplemented with further safety mechanisms: easy filtering, for instance, shouldn’t be sufficient to efficiently stop points like immediate injection.
Sandboxing Execution Environments
Docker containers and Wasm sandboxes are nice methods to isolate agent-generated code earlier than confirming there aren’t any potential compromises in it. That is efficient towards unsafe code execution, however added measures are nonetheless wanted to safe actions that contain exterior APIs or enterprise methods.
Designing Human-in-the-Loop (HITL) Checkpoints
Simplicity is usually the simplest technique, and HITL practices are a transparent instance of this. Mainly, this consists of letting brokers function on their very own for low-stakes actions like retrieving and summarizing data, whereas requiring specific human verification earlier than conducting high-stakes or irreversible ones, similar to monetary transactions.
Monitoring and Auditing Agent Exercise
Usually, from a safety standpoint, AI brokers have to be handled as privileged software program entities slightly than as purely clever assistants. To take action, logging prompts, permission requests, approval choices, calls to instruments, and exterior actions is an crucial follow. Mixed with complete monitoring, that is very important to detect vulnerabilities and threats like immediate injection makes an attempt, undesired software utilization, and different coverage violations.
Closing Remarks: Trying Forward
In step with the rising degree of sophistication attained by agentic AI methods, organizations also needs to concentrate on rising dangers like software misuse and immediate injection. This text outlined these two salient safety issues in agentic AI and underlined a number of methods to remember to confidently deploy autonomous methods fueled by AI brokers in the actual world, attaining each productiveness and safety.
On this article, you’ll be taught what immediate injection and gear misuse are within the context of agentic AI methods, and which protection methods consultants advocate to mitigate them.
Subjects we’ll cowl embody:
- How immediate injection and gear misuse can compromise AI brokers deployed in real-world manufacturing environments.
- Why conventional safety mechanisms fall quick towards methods that may cause, plan, and act autonomously.
- 5 foundational protection methods, starting from least privilege and sandboxed execution to human-in-the-loop checkpoints.
Let’s not waste any extra time.
Introduction
There may be an ongoing speedy transition of AI brokers from experimental settings into real-world manufacturing environments. This brings about important shifts in brokers’ capabilities, which naturally raises safety issues. The occasions of coping with chatbots that may unintentionally hallucinate or generate delicate textual content are just about gone: now, probably the most distinguished AI methods are outfitted with autonomous brokers with the “added capabilities” of studying your databases — supplied that you just configure the required permissions and authorizations, after all — sending emails, executing code scripts, and, usually, taking your function in interacting with exterior parts and methods.
Among the best-known safety frameworks for agentic AI is the OWASP High 10 for AI Brokers, which constitutes a sensible strategy for understanding how conventional safety mechanisms and assumptions begin to lose their cause for being towards AI methods that may cause, plan, make choices, and act on their very own.
This text outlines two of probably the most salient vulnerabilities that compromise agent-based purposes as we speak, particularly immediate injection and gear misuse, and discusses methods at present being proposed by discipline consultants to deal with them successfully.
The Threats: Immediate Injection and Instrument Misuse
Let’s briefly talk about the 2 “twin threats” that turn into important once more once we give AI methods the flexibility to behave by themselves, with the possibility of profitable assaults growing notably:
Immediate Injection
This follow shouldn’t be unique to agentic AI methods, being additionally current in conventional conversational AI purposes. Immediate injection arises when untrusted inputs to a language mannequin are interpreted as directions slightly than mere knowledge. This causes fashions to float from their common, supposed habits. This downside has been renamed Agent Objective Hijacking within the context of agentic AI and AI safety vulnerabilities. The strategy is as follows: an attacker might embed malicious directions throughout the physique of emails, net pages, or every other paperwork processed by an agent. Thus, given language fashions’ inadequate potential to successfully differentiate trusted directions from untrusted, exterior ones, attackers can ultimately redirect brokers removed from their supposed purpose.
Instrument Misuse
Also referred to as the “confused deputy” vulnerability, this happens when a extremely privileged and trusted system often known as the deputy will get tricked by a person with fewer privileges into misusing its permissions. As brokers depend on quite a lot of each inside and exterior instruments to perform duties, once they mistakenly (and unknowingly) leverage reputable permissions to carry out dangerous or unauthorized actions primarily based on an attacker’s intentions, the implications may be disproportionate: from exposing delicate data to triggering cascading failures throughout a number of linked purposes.
The Protection Methods
Most conventional community safety protocols fall quick in efficiently securing entities with autonomous reasoning and appearing capabilities. For that reason, it’s essential to outline novel architectures that may govern not solely brokers’ habits but in addition overarching system permissions.
These are a few of the foundational protection methods which can be deemed efficient by consultants within the discipline. They’ll typically be applied utilizing mature, open-source applied sciences, with out the need of resorting to costly proprietary options.
Imposing Strict Least Privilege
This technique boils right down to giving brokers solely the strictly required capabilities and permissions. An agent constructed for studying buyer assist tickets ought to under no circumstances have the flexibility to modify manufacturing databases, as an example. To implement this, think about Identification and Entry Administration (IAM) mechanisms to limit entry to datasets, APIs, and operations, ideally isolating tasks amongst specialised brokers to cut back the chance and affect of vulnerabilities.
Implementing Open-Supply Guardrails
NVIDIA NeMo Guardrails and Meta Llama Guard are two notable examples of such open-source options that assist implement security protocols and mitigate publicity. Keep in mind, although, that guardrails are only one protection layer that could be supplemented with further safety mechanisms: easy filtering, for instance, shouldn’t be sufficient to efficiently stop points like immediate injection.
Sandboxing Execution Environments
Docker containers and Wasm sandboxes are nice methods to isolate agent-generated code earlier than confirming there aren’t any potential compromises in it. That is efficient towards unsafe code execution, however added measures are nonetheless wanted to safe actions that contain exterior APIs or enterprise methods.
Designing Human-in-the-Loop (HITL) Checkpoints
Simplicity is usually the simplest technique, and HITL practices are a transparent instance of this. Mainly, this consists of letting brokers function on their very own for low-stakes actions like retrieving and summarizing data, whereas requiring specific human verification earlier than conducting high-stakes or irreversible ones, similar to monetary transactions.
Monitoring and Auditing Agent Exercise
Usually, from a safety standpoint, AI brokers have to be handled as privileged software program entities slightly than as purely clever assistants. To take action, logging prompts, permission requests, approval choices, calls to instruments, and exterior actions is an crucial follow. Mixed with complete monitoring, that is very important to detect vulnerabilities and threats like immediate injection makes an attempt, undesired software utilization, and different coverage violations.
Closing Remarks: Trying Forward
In step with the rising degree of sophistication attained by agentic AI methods, organizations also needs to concentrate on rising dangers like software misuse and immediate injection. This text outlined these two salient safety issues in agentic AI and underlined a number of methods to remember to confidently deploy autonomous methods fueled by AI brokers in the actual world, attaining each productiveness and safety.