The Belief Drawback Connecting Authorities Breaches and AI Agent Assaults
Probably the most harmful level in enterprise safety proper now shouldn’t be the community perimeter. It’s the second a trusted system accepts an id, a doc, a webpage, or an instruction and decides to behave on it.
Two tales from mid-2026 make the purpose from reverse ends of the know-how stack. One includes a federal information-sharing platform working for twenty years. The opposite includes AI brokers studying bizarre net content material. Neither story brought about the opposite. Collectively they expose the identical operational hole: organizations hold granting trusted entry quicker than they’ll confirm it.
What the HSIN Incident Establishes
The Division of Homeland Safety confirmed in late June hackers had accessed the Homeland Safety Data Community. Federal, state, native, tribal, territorial, worldwide, and private-sector companions use the platform to share delicate however unclassified info and coordinate emergency response. A DHS spokesperson described the goal as “a particular, unclassified legacy info sharing atmosphere,” and pressured categorized networks confirmed no indicators of influence, in accordance with Nextgov/FCW, which first reported the breach.
Two individuals accustomed to the investigation advised Nextgov/FCW the intrusion possible occurred between late Could and early June. The hackers reportedly focused HSIN servers together with a SharePoint system the company makes use of for collaboration. Investigators had not established the attacker’s id, affiliation, or motive as of early July, and had not confirmed whether or not any documentation left the platform.
Senate Intelligence Committee Vice Chair Mark Warner raised the stakes additional. In a public assertion coated by TechCrunch, Warner famous HSIN was actively supporting safety coordination for the World Cup video games underway throughout america. The platform had additionally helped handle the response to final 12 months’s midair collision between an American Airways jet and an Military Black Hawk helicopter close to Washington, D.C. Public reporting has not confirmed attackers considered or eliminated any particular operational plans tied to both occasion. The Home Homeland Safety Committee has requested a briefing, a step signaling how severely Congress views a platform of such scope going unmonitored for weeks.
None of it’s new territory for HSIN. Nextgov/FCW beforehand reported a 2023 contractor coding error uncovered restricted HSIN knowledge, together with delicate private info, to customers who ought to by no means have had entry. Deal with the 2023 incident as a previous misconfiguration reasonably than proof linked to the 2026 breach. The sample throughout the 2 incidents nonetheless holds: a platform constructed to serve a large, distributed accomplice base accumulates entry relationships quicker than anybody revalidates them.
Immediate Injection Turns Content material Into an Assault Floor
Palo Alto Networks’ Unit 42 revealed analysis in March describing one thing safety groups had principally mentioned solely in principle. Oblique immediate injection assaults have been working in opposition to AI brokers on stay web sites. Attackers embed hidden directions inside ordinary-looking content material, then look forward to an AI agent to learn the content material whereas performing a reliable process.
Unit 42 catalogued 22 distinct strategies attackers use to hide such payloads inside net pages, together with plaintext directions, HTML attribute cloaking, and CSS-based hiding. Documented attacker intent coated ad-review evasion, search manipulation, knowledge destruction, denial of service, unauthorized transactions, and leakage of system prompts or delicate info. Unit 42 stated it had not confirmed a case the place a deployed ad-checking agent was compromised by the particular payload it cited, an essential distinction between an tried assault and a accomplished breach.
The mechanism issues greater than any single payload. An AI agent studying webpages, emails, code feedback, or instrument output whereas holding permission to ship messages, approve transactions, or modify data treats attacker-supplied textual content as a possible instruction reasonably than as inert content material. Unit 42’s steerage calls model-level guardrails “mushy” defenses and recommends laborious controls as a substitute, notably strict limits on what instruments an agent can invoke.
The Shared Failure Is Unbounded Belief
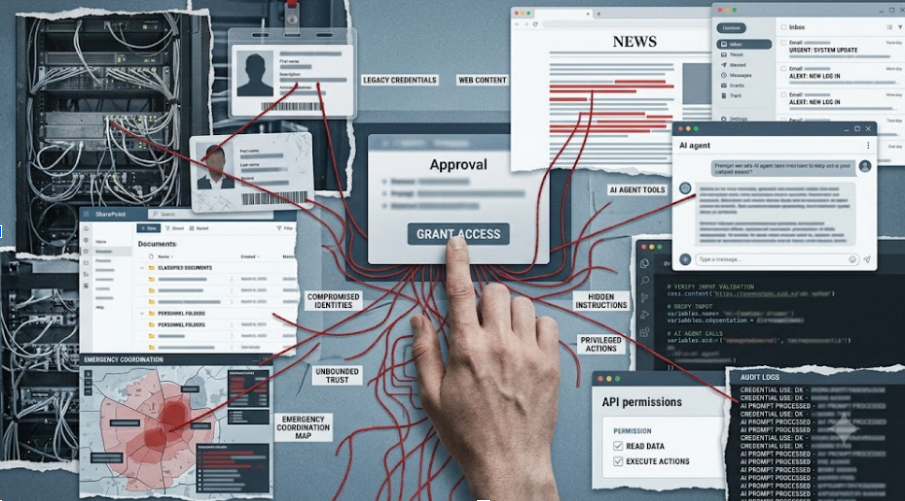
Line up the 2 incidents and 4 weaknesses repeat throughout them:
- Broad entry relationships. HSIN connects a large, ongoing group of accomplice businesses and contractors. AI brokers more and more hook up with electronic mail, repositories, browsers, databases, and enterprise APIs.
- Inputs assumed reliable with out steady checking. A legitimate HSIN account will be compromised lengthy earlier than anybody notices. A legitimate-looking webpage can carry a hidden instruction an agent will comply with.
- Permission scope exceeding process scope. A contractor account, service credential, or AI agent retaining entry past its instant job multiplies the injury a single compromise may cause.
- Weak visibility on the motion degree. Normal logs can present a sound account or agent making a request with out revealing an attacker manipulated the intent behind it.
Safety packages nonetheless are inclined to assign the 2 issues to separate groups: one for legacy infrastructure, one other for AI governance. The ensuing division produces blind spots precisely the place an attacker solely wants one weak id, one stale system, or one hidden instruction to transform trusted entry into an assault path.
AI Compresses the Attacker’s Work Cycle
Google’s Risk Intelligence Group reported in Could it had recognized what it believed to be the primary zero-day exploit developed with AI help. The exploit focused a two-factor authentication bypass in an open-source system administration instrument. GTIG labored with the seller to reveal the flaw and disrupt the exercise earlier than the risk actor may use it at scale. The group linked broader curiosity in AI-driven vulnerability discovery to actors related to China and North Korea, and documented AI-assisted malware improvement, together with tooling producing instructions from mannequin output at runtime.
None of it means each attacker all of a sudden operates at nation-state sophistication. The extra correct learn: AI shortens the analysis and iteration cycle attackers depend on. Testing variations in opposition to a goal now prices much less time and fewer effort. Defenders, in the meantime, nonetheless cope with change-control processes, vendor dependencies, incomplete asset inventories, and permission opinions transferring on a quarterly cycle at greatest. The asymmetry is structural, not common: attackers can check broadly and quick, whereas defenders carry the accrued weight of each id, system, and integration a enterprise has ever added.
One Management Mannequin for Legacy Techniques and AI Brokers
Operating separate playbooks for “conventional infrastructure” and “AI safety” now not holds up. All sides wants the identical disciplines.
Map each belief path, not simply each asset. Doc which people, service accounts, contractors, federated companions, OAuth grants, API keys, and AI brokers can learn, change, approve, ship, delete, or buy, and document it for every one reasonably than for the system as an entire.
Lower privilege on the motion degree. Separate learn entry from write entry for AI instruments: an agent summarizing electronic mail doesn’t want permission to ship it, and an agent reviewing code doesn’t want deployment credentials. Apply the identical logic to legacy platforms by eradicating stale accounts and revalidating contractor and accomplice entry on a set schedule.
Deal with retrieved content material as hostile by default. AI programs ought to mark the provenance of webpages, paperwork, messages, and gear output, and forestall the content material from instantly triggering privileged capabilities.
Require a human to approve high-impact actions: exterior communication, funds, credential adjustments, manufacturing deployment, knowledge deletion, entry grants, and bulk document adjustments. The approval display screen wants to indicate the precise motion, goal, and parameters. A button labeled merely “approve process” provides you no actual management.
Watch conduct, not simply logins. New entry patterns, uncommon downloads, repeated failed instrument calls, and an agent reaching for a website no one authorized all deserve consideration earlier than they change into an incident report.
Pink-team the entire workflow on a recurring foundation, together with retrieved content material, reminiscence, plugins, linked servers, and the approval circulation itself, not simply the underlying mannequin.
Design for containment on the idea one account or agent will finally misbehave. Scoped tokens, short-lived credentials, per-task sandboxes, and speedy revocation restrict how far a single unhealthy actor or unhealthy immediate can journey.
Metrics Operators Can Use
You don’t want a brand new division to start out closing the hole. Monitor a small variety of figures telling you whether or not belief will get verified:
- Share of privileged accounts reviewed within the final 90 days
- Variety of dormant accomplice, contractor, or service accounts nonetheless holding entry
- Share of AI brokers with write-capable instruments, and what number of require approval for high-impact actions
- Imply time to revoke an uncovered id or integration
- Protection of action-level logging throughout legacy programs and AI brokers
Not one of the metrics above require unique tooling. Most organizations have already got the info. What they lack is the behavior of asking the query on a set schedule as a substitute of after an incident forces the assessment.
HSIN and the prompt-injection payloads Unit 42 documented didn’t come from the identical attacker, the identical exploit, and even the identical decade of know-how. Line them up anyway and the lesson holds: no id, system, mannequin, doc, or agent ought to carry extra belief than the duty in entrance of it requires, and each consequential motion wants to remain observable and reversible. Organizations hold treating legacy infrastructure and AI safety as separate disciplines, and they’re going to hold discovering the hole the identical means DHS did: after the actual fact.